The Invisible Networking Bill
Compute costs are obvious. Storage costs are steady. But networking costs are the silent, sudden killers of cloud budgets. It is entirely common for an organization to migrate to the cloud, optimize their EC2 instances, rightsize their databases, and then be blindsided by a $50,000 monthly charge labeled simply "Data Transfer Out."
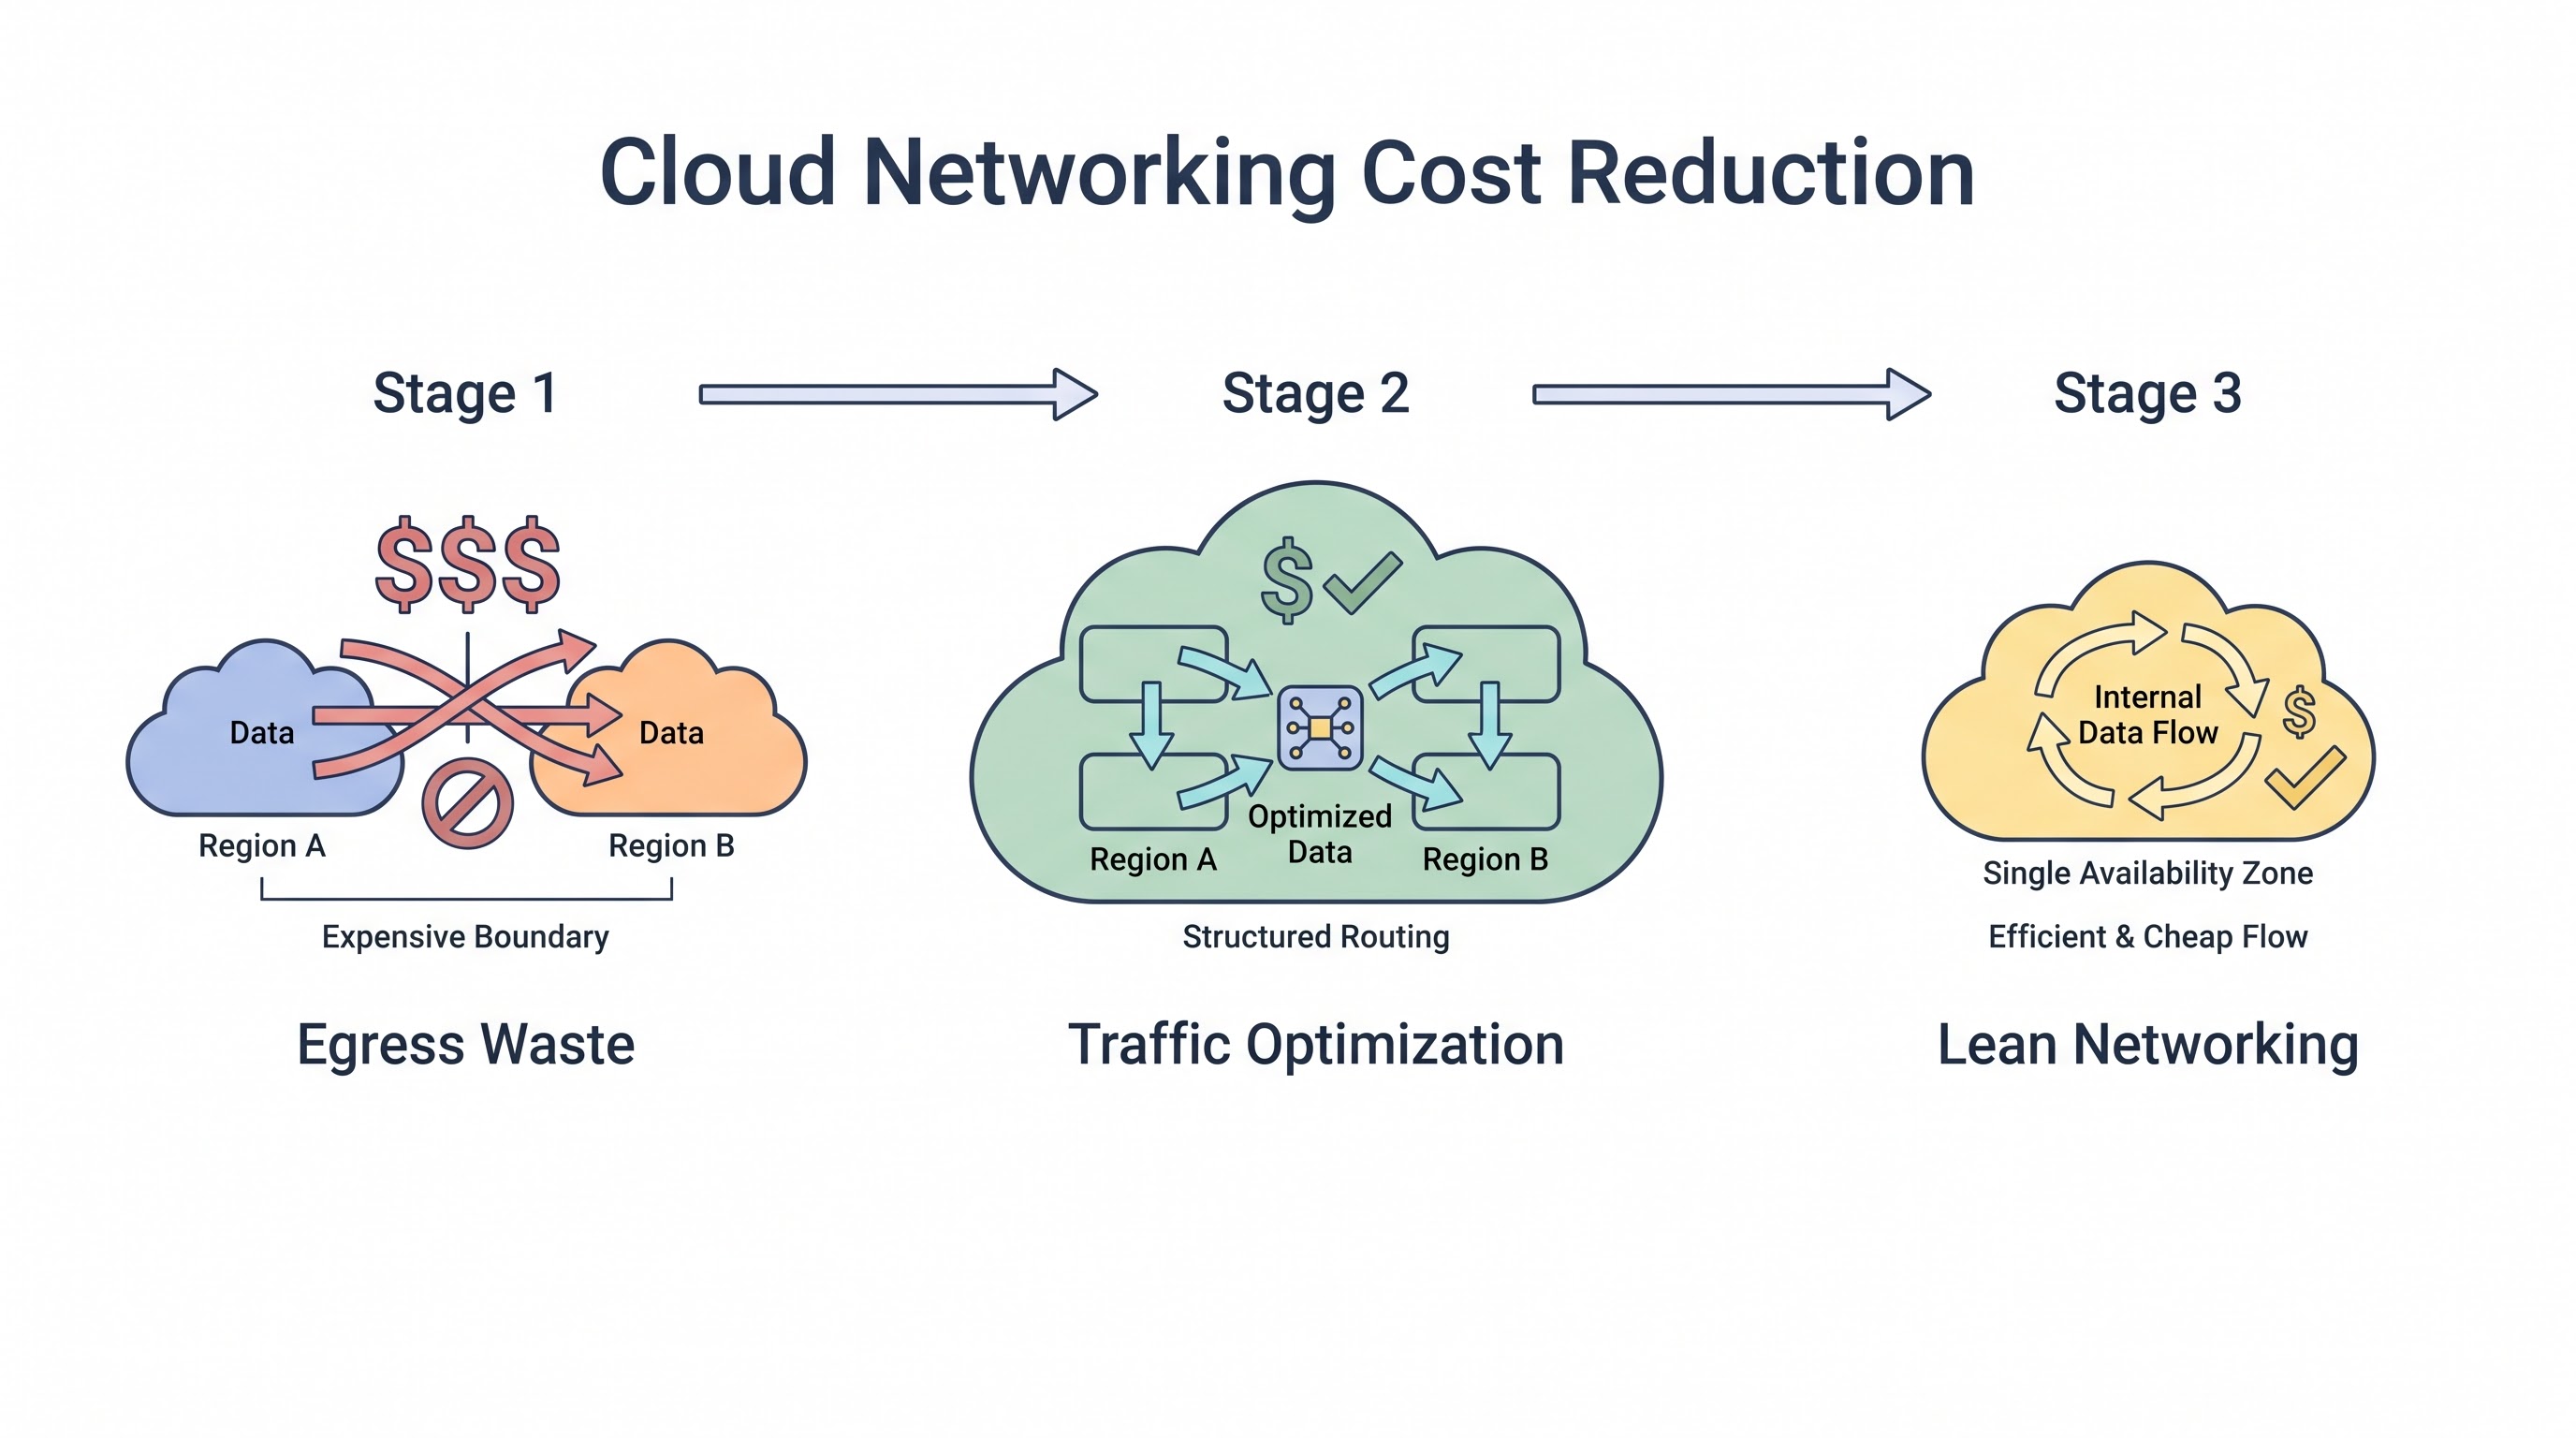
Cloud networking pricing is notoriously complex, highly granular, and designed to penalize specific architectural patterns. You do not just pay for bandwidth; you pay for how data travels. Data crossing an Availability Zone boundary costs money. Data traveling through a managed gateway costs money. Data leaving the cloud costs a premium.
This guide dissects the mechanics of cloud networking costs, providing the architectural patterns required to slash your data transfer bill without compromising performance or security.
The Rules of Cloud Data Transfer
While the exact pricing varies slightly between AWS, Azure, and GCP, the fundamental economic rules are identical across all major providers:
Data In is Free: The providers want your data. Ingress (bringing data into the cloud) is almost always free.
Data Out is Expensive: Egress (sending data out to the internet or an on-premises datacenter) is heavily taxed.
Crossing Zones Costs Money: Data transfer between two EC2 instances in the same Availability Zone (AZ) using private IP addresses is free. If those instances are in different AZs within the same region, you pay a per-GB charge.
Public IPs Cost More: If two instances in the same VPC communicate using their Public IP addresses, the traffic is routed out to the internet and back in. You will be charged egress rates, even if the instances are sitting in the same physical datacenter. Always use private IPs for internal routing.
The NAT Gateway Trap
The single largest networking cost anomaly in modern cloud architectures is the Managed NAT Gateway (e.g., AWS NAT Gateway, Azure NAT Gateway).
For security, backend servers (like application servers or database nodes) must reside in private subnets with no public IP addresses. However, these servers often need internet access to download OS patches or communicate with third-party APIs (like Stripe or Twilio). The architectural solution is routing their outbound traffic through a NAT Gateway located in a public subnet.
The Trap: Cloud providers charge an hourly fee for the NAT Gateway, plus a per-GB data processing charge for every byte that flows through it. If a fleet of EC2 instances in a private subnet downloads 100 Terabytes of data from an S3 bucket via the public internet routing through a NAT Gateway, the processing fees will be astronomical.
The Solution: VPC Endpoints (PrivateLink)
The primary way to bypass the NAT Gateway trap is utilizing VPC Endpoints (AWS PrivateLink, Azure Private Link).
A VPC Endpoint allows resources in your private subnet to connect to cloud provider services (like S3, DynamoDB, or Kinesis) directly over the provider's internal backbone network. The traffic never touches the public internet, and crucially, it never passes through the NAT Gateway.
Gateway Endpoints: (Specific to AWS S3 and DynamoDB). These are essentially free routing table updates. If you have high traffic to S3 from private subnets, enabling a Gateway Endpoint is an immediate, zero-cost FinOps win.
Interface Endpoints: These deploy an Elastic Network Interface (ENI) into your subnet. They carry a small hourly fee and a lower per-GB processing fee than a NAT Gateway, but are significantly cheaper and more secure for accessing services like KMS or EventBridge.
Cross-AZ Traffic: The Hidden Multiplier
High Availability requires deploying architecture across multiple Availability Zones (AZs). However, if your web servers are in AZ-A, but your primary database node is in AZ-B, every single database query incurs cross-AZ data transfer charges.
In highly chatty microservice architectures (like Kubernetes clusters), cross-AZ costs can rapidly escalate. If "Service X" continuously polls "Service Y", and the Kubernetes scheduler randomly places those pods in different AZs, you pay for every poll.
The Mitigation:
Zone Affinity: Configure your Load Balancers and Kubernetes routing rules to prefer routing traffic to destinations within the same AZ whenever possible.
Consolidate Chatty Services: If two microservices transfer massive amounts of data between each other constantly, consider combining them, or ensuring they are scheduled on nodes within the same AZ.
CDNs: The Ultimate Egress Hack
If your application serves large static assets (images, video, Javascript files) from S3 or an EC2 web server directly to users on the internet, you are paying premium egress rates.
The solution is a Content Delivery Network (CDN) like Amazon CloudFront, Cloudflare, or Fastly. Cloud providers heavily incentivize CDN usage. For example, data transfer from AWS S3 to AWS CloudFront is completely free. You then only pay the CloudFront egress rate, which is significantly cheaper than the direct S3 egress rate. By caching assets at the edge, a CDN not only slashes latency but can reduce your total data transfer bill by 40-60%.
Transit Gateways and Peering
In enterprise multi-account environments, networks must be connected.
VPC Peering: Connecting two VPCs directly. Data transfer is charged at standard cross-AZ rates. This is cost-effective for simple, 1-to-1 connections.
Transit Gateways: A central hub that connects thousands of VPCs and on-premises networks. While operationally simpler, Transit Gateways carry an additional per-GB processing fee. Do not route massive, continuous data flows (like database replication) through a Transit Gateway if a direct VPC Peering connection will suffice.
Key Takeaway
Cloud networking costs penalize inefficient architecture. Never use public IP addresses for internal routing. Scrutinize your NAT Gateway usage; it is often the source of massive billing anomalies. Implement VPC Endpoints to route traffic to native cloud services over the internal backbone for free. Enforce zone affinity in your routing layers to minimize cross-AZ chat, and put a CDN in front of any internet-facing asset to drastically lower egress rates.
All in One Place
Atler Pilot decodes your cloud spend story by bringing monitoring, automation, and intelligent insights together for faster and better cloud operations.