The End of the ClickOps Era
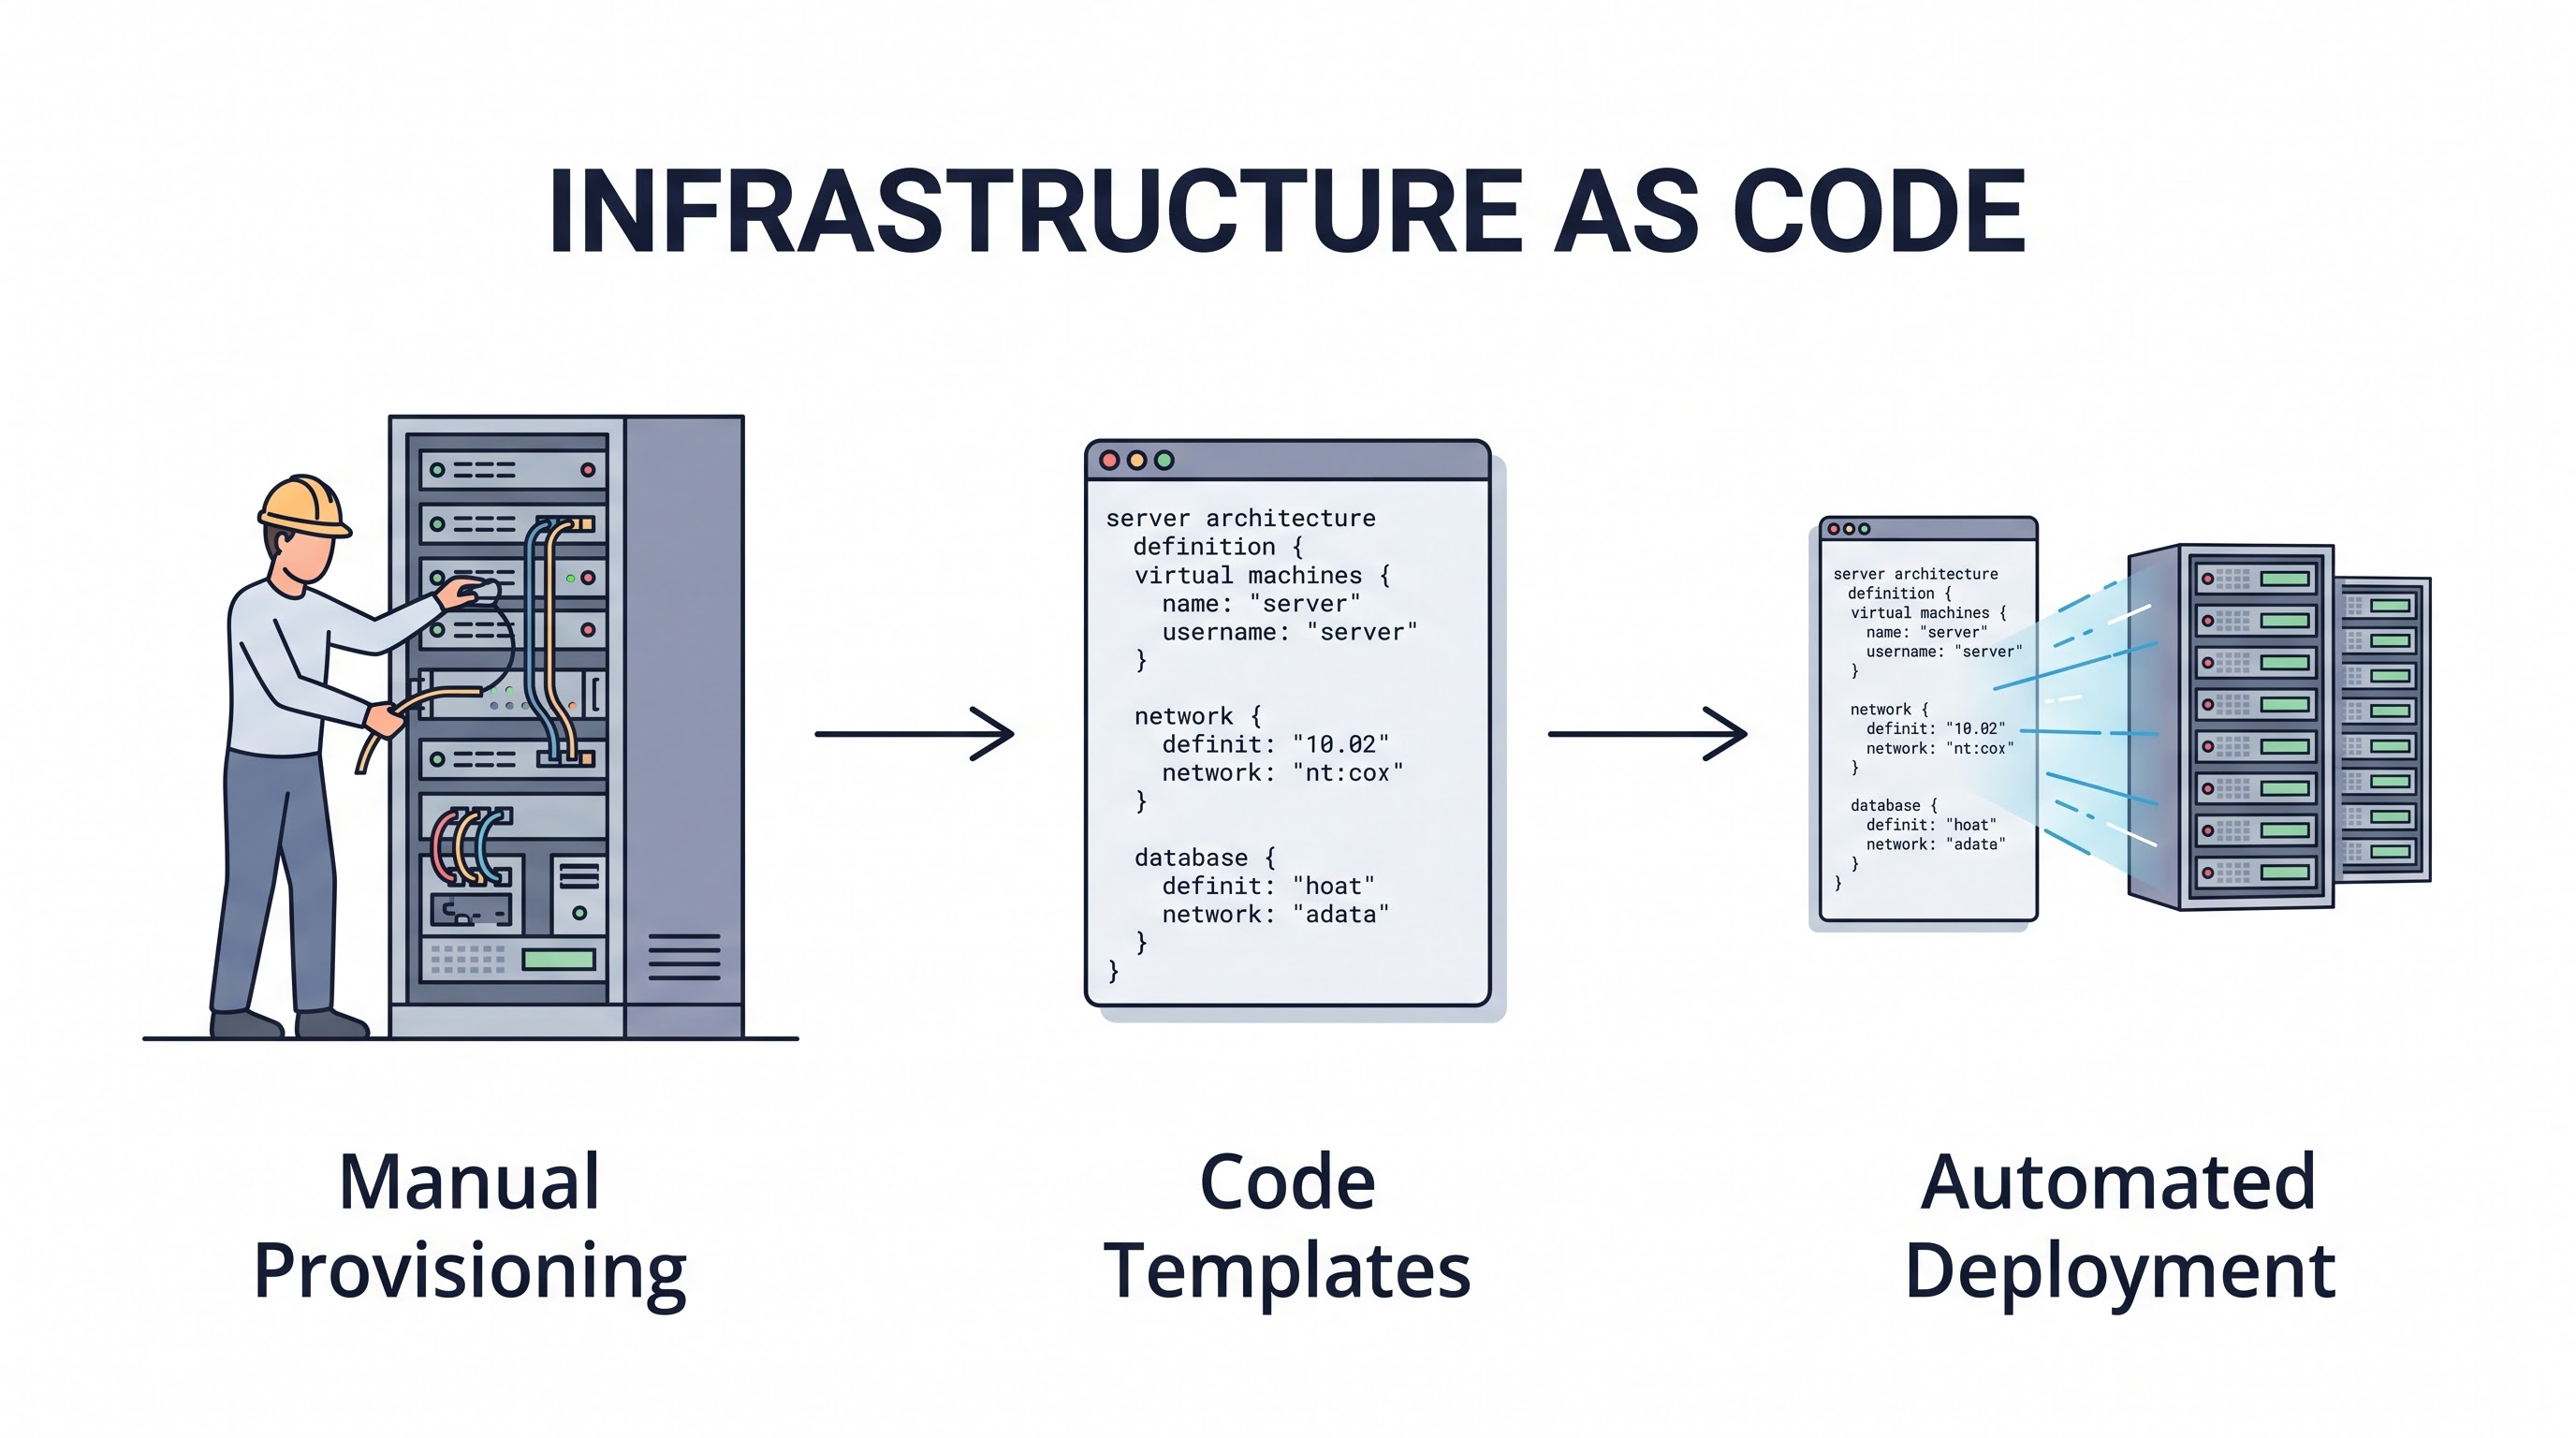
Historically, provisioning a server involved racking physical hardware. The cloud digitized this process, allowing engineers to provision massive fleets of virtual machines by clicking buttons in a web console. This practice—colloquially known as "ClickOps"—is the enemy of scale, reliability, and security.
If an environment is built via the console, it cannot be reliably replicated. It cannot be audited. If a disaster occurs, rebuilding the architecture relies entirely on an engineer's memory. In modern cloud operations, clicking through a console to deploy production infrastructure is an unacceptable risk.
The solution is Infrastructure as Code (IaC). IaC is the foundational technology that enables everything from automated security scanning to rapid disaster recovery. This guide explores the core principles of IaC, state management, and the shifting battleground between the leading tools in 2026.
The Definition of IaC
Infrastructure as Code is exactly what it sounds like: writing code to define and manage infrastructure. Instead of manually creating a VPC, subnets, and an RDS database, an engineer writes a configuration file detailing those resources. An IaC engine reads the file, calls the cloud provider's APIs, and provisions the resources precisely as defined.
This unlocks the superpower of the cloud era: treating infrastructure identically to application code. IaC files are stored in Git. Changes to the infrastructure require a Pull Request, a peer review, and automated testing before being merged and deployed via a CI/CD pipeline.
Declarative vs. Imperative IaC
The IaC ecosystem is divided by two fundamental philosophies.
Declarative IaC (What you want): You define the desired end state of the infrastructure. You tell the tool, "I want three EC2 instances." If you currently have zero, the tool creates three. If you currently have five, the tool deletes two. You do not write the logic of how to achieve this; the IaC engine calculates the difference between reality and the desired state. (Examples: Terraform, CloudFormation).
Imperative IaC (How to do it): You define the specific steps required to achieve the end state using a standard programming language (Python, TypeScript). You write logic: "If instances < 3, run create_instance() loop." (Example: Pulumi, AWS CDK).
Terraform: The Industry Standard
HashiCorp's Terraform (and its open-source fork, OpenTofu) is the undisputed heavyweight champion of declarative IaC.
The Pros: It is cloud-agnostic. The exact same workflow (and the HCL configuration language) can provision AWS, Azure, GCP, Datadog alerts, and GitHub repositories via specialized "providers." It has a massive community and a module for almost every conceivable architecture.
The Cons: HCL (HashiCorp Configuration Language) is a proprietary, domain-specific language. While it has added logic capabilities (for loops, conditionals) over time, it is not a fully-fledged programming language, which can make highly complex, dynamic deployments frustrating for software engineers.
Pulumi: Infrastructure as Software
Pulumi represents the evolution of IaC toward "Infrastructure as Software."
The Pros: It allows developers to define infrastructure using languages they already know (TypeScript, Python, Go, C#). This enables standard software engineering practices—unit testing infrastructure, using standard package managers (npm, pip), and creating highly complex, dynamic infrastructure logic using standard
if/elsestatements and loops.The Cons: Because it is full code, it can be overly complex for simple deployments. It requires the operations team to be proficient in software engineering, blurring the lines between dev and ops.
CloudFormation & ARM: The Native Options
Cloud providers offer their own native declarative tools: AWS CloudFormation, Azure Resource Manager (ARM/Bicep), and GCP Cloud Deployment Manager.
The Pros: Zero third-party dependencies. They are deeply integrated into the provider's ecosystem and often support new services on day one. They manage state internally, removing a major operational headache.
The Cons: They lock you into that specific cloud provider. Writing raw CloudFormation (JSON/YAML) is notoriously verbose and difficult to maintain, driving the adoption of higher-level abstractions like the AWS Cloud Development Kit (CDK), which compiles TypeScript/Python down to CloudFormation.
The Peril of State Management
Both Terraform and Pulumi rely on a "State File." This file is a snapshot of the infrastructure as the tool currently understands it. When you run a deployment, the engine compares the code against the state file to determine what needs to change.
Critical Best Practice: The state file is the most dangerous file in your organization. If it is deleted, the IaC tool loses track of the infrastructure. Furthermore, the state file often contains secrets (database passwords) in plaintext. You must never commit a state file to a local Git repository. It must be stored in a secure, encrypted, remote backend (like an S3 bucket with versioning enabled and DynamoDB state locking) or a managed SaaS offering (Terraform Cloud, Pulumi Cloud).
Handling Infrastructure Drift
Infrastructure drift occurs when the actual configuration in the cloud differs from the code defined in Git. This usually happens when an engineer logs into the AWS console at 2:00 AM to manually fix an issue (ClickOps) but forgets to update the Terraform code.
The next time the CI/CD pipeline runs, the IaC tool will detect the drift and forcefully revert the manual change, potentially causing an outage. Mature organizations run automated drift detection checks daily. If drift is detected, an alert is fired immediately, forcing the team to either import the manual change into the code or revert the console action.
Key Takeaway
Infrastructure as Code is mandatory. ClickOps is dead. For multi-cloud environments and teams with strong operations backgrounds, Terraform remains the gold standard. For development teams that prefer treating infrastructure identically to application code, Pulumi or AWS CDK are superior. Regardless of the tool, secure your state files rigorously and implement continuous drift detection to ensure your code always represents reality.
All in One Place
Atler Pilot decodes your cloud spend story by bringing monitoring, automation, and intelligent insights together for faster and better cloud operations.