The Networking Labyrinth
For most developers transitioning to Kubernetes, the compute model (Pods and Deployments) is relatively intuitive. The networking model, however, is a labyrinth. How does a request from a user in London navigate through a cloud load balancer, find the correct worker node, traverse into a virtualized container network, and hit the exact correct Pod, when that Pod's IP address changes every three days?
Kubernetes abstracts networking behind multiple layers of software-defined routing (kube-proxy, CoreDNS, Ingress Controllers, CNI plugins). While this abstraction provides immense flexibility, misconfiguring it leads to dropped connections, massive cross-AZ latency costs, and severe security vulnerabilities.
This guide demystifies Kubernetes networking, explaining how traffic flows into, out of, and within the cluster, and explores the advanced capabilities of Service Meshes.
The Fundamental Rule: Flat Networking
The foundational principle of Kubernetes networking is that every Pod gets its own unique IP address, and every Pod can communicate with every other Pod across all nodes without using Network Address Translation (NAT).
This "flat" network is implemented by a Container Network Interface (CNI) plugin (like Calico, Flannel, or AWS VPC CNI). To the application developer, the network behaves as if all containers were plugged into the same giant physical switch, regardless of the underlying cloud VPC configuration.
Services: Stable IPs in a Sea of Ephemerality
Pods are ephemeral. They crash, scale up, and are replaced. You cannot rely on a Pod's IP address. If the "Frontend" needs to talk to the "Backend," hardcoding the Backend's Pod IPs is a guaranteed failure.
Kubernetes solves this with the Service object. A Service provides a stable, permanent virtual IP address (ClusterIP) and a DNS name (managed by CoreDNS) that acts as an internal load balancer. The Frontend sends its request to http://backend-service.default.svc.cluster.local. The Service intercepts the request and routes it to one of the currently healthy Backend Pods. kube-proxy handles the low-level IP tables routing on each node to make this magic happen.
Ingress: Routing Traffic Into the Cluster
A ClusterIP Service is only accessible from inside the cluster. To expose a web application to the public internet, you need an entry point.
NodePort / LoadBalancer Services: The legacy methods. A
LoadBalancerservice tells the cloud provider (AWS/Azure) to spin up a physical cloud load balancer for that specific service. If you have 50 microservices, spinning up 50 cloud load balancers is financially ruinous.Ingress Controllers: The modern standard. An Ingress Controller (like NGINX Ingress, Traefik, or AWS ALB Ingress) is a specialized pod that acts as a reverse proxy. You provision a single cloud load balancer that routes all public traffic to the Ingress Controller. The controller reads the HTTP headers (e.g., "Route
/apito the API Service, route/webto the Web Service") and routes the traffic internally. It handles SSL termination and URL routing efficiently.
Egress: Routing Traffic Out of the Cluster
By default, Pods can access the external internet through the node's NAT gateway. However, in secure enterprise environments, this is a severe risk.
If a Pod is compromised, you do not want it downloading malware from the internet. Controlling egress requires specialized configurations:
Egress Gateways: Forcing all outbound traffic to flow through a specific node or proxy, allowing the security team to inspect the traffic and apply static IP whitelisting for third-party SaaS integrations.
Network Policies: Internal Firewalls
As noted, the fundamental rule of Kubernetes is that every pod can talk to every other pod. From a security perspective, this is terrifying. If a low-level pod is breached, the attacker can scan the entire cluster.
Network Policies are the internal firewalls of Kubernetes. They are YAML rules that dictate allowed traffic flow. You must implement a "Default Deny" posture in every namespace, isolating all pods, and then explicitly write policies to allow necessary traffic (e.g., "Only allow traffic to the Database Pod if it originates from a pod with the label app: frontend").
The Next Evolution: The Service Mesh
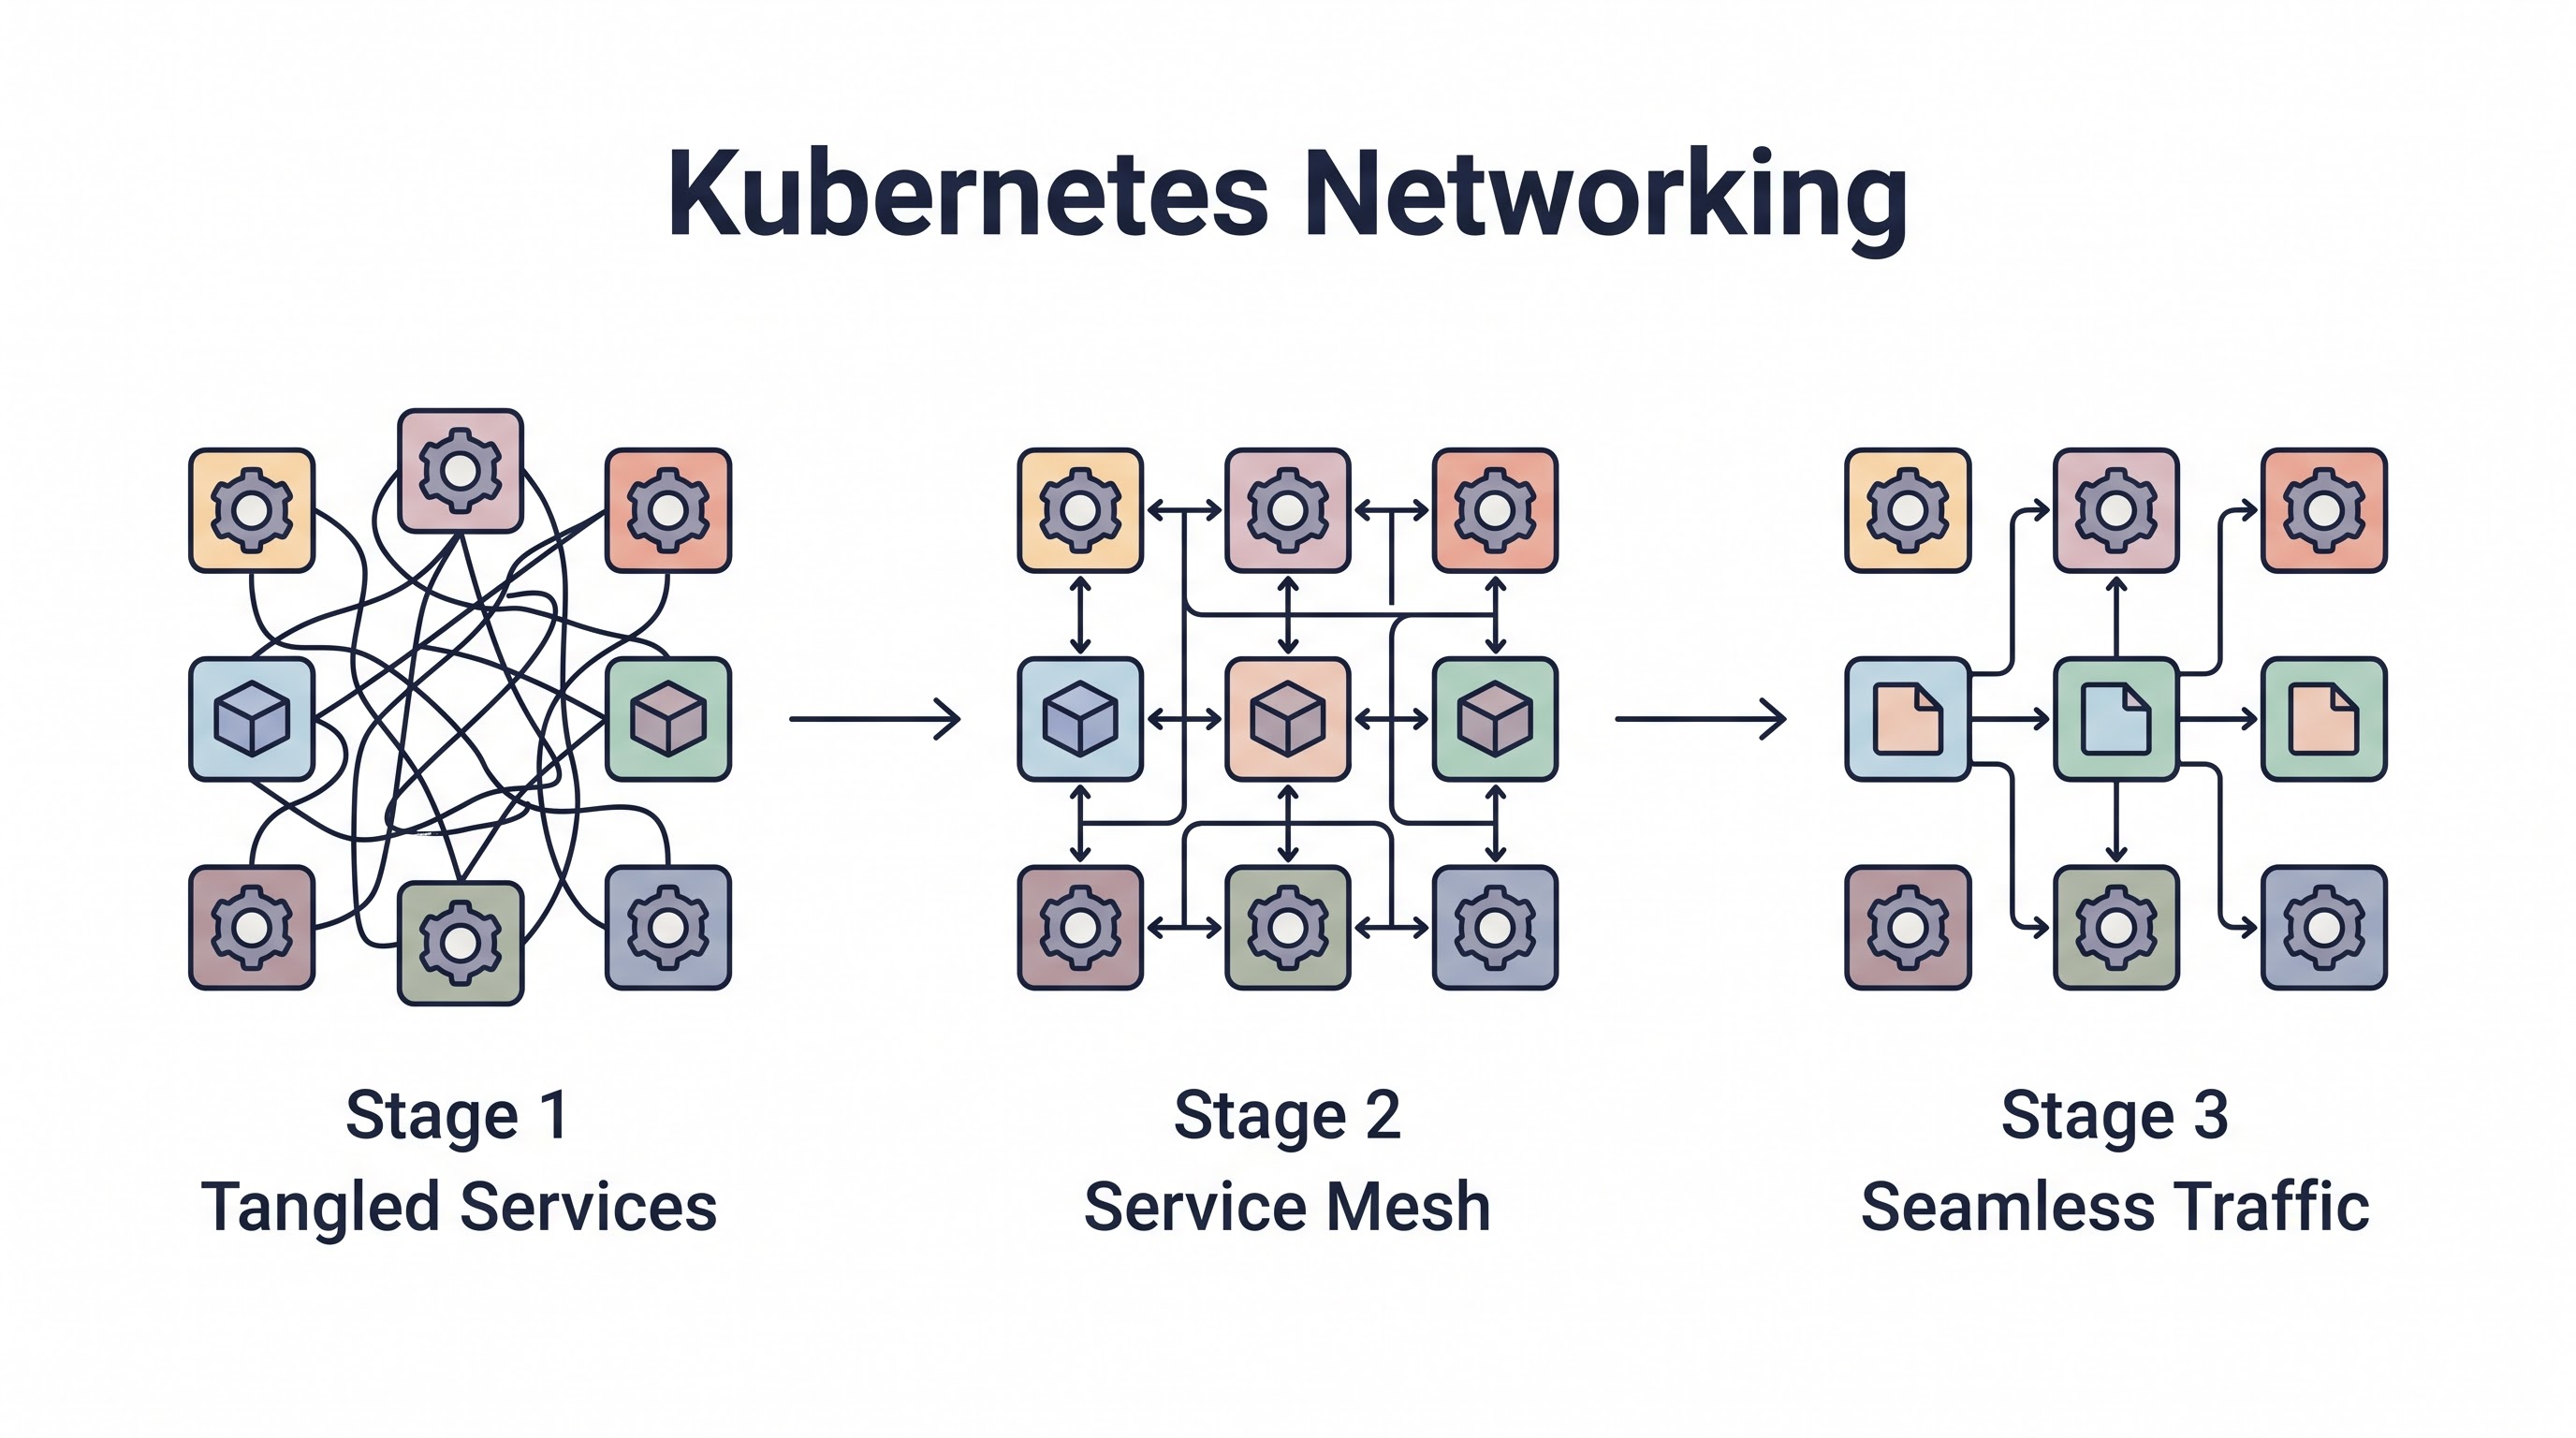
As organizations scale to hundreds of microservices, native Kubernetes networking (Services and Ingress) hits its limits. It lacks advanced capabilities like traffic shaping, automatic retries, circuit breaking, and deep observability.
The solution is the Service Mesh (like Istio or Linkerd). A service mesh injects a tiny proxy (a "sidecar," like Envoy) into every single Pod. Instead of the application container talking to the network, the application container talks to its sidecar, and the sidecar handles the network.
The Service Mesh provides massive architectural advantages:
Mutual TLS (mTLS): The sidecars automatically encrypt and authenticate all traffic between pods, fulfilling the core requirement of Zero Trust Architecture without requiring developers to write complex certificate management code.
Advanced Routing (Canary Deployments): The mesh can seamlessly route 95% of traffic to version 1.0 of a service, and 5% of traffic to version 1.1 for testing, enabling highly complex deployment strategies.
Observability: Because the sidecar intercepts every network packet, it automatically generates massive amounts of telemetry data (metrics and distributed traces), providing total visibility into the network performance without altering application code.
Key Takeaway
Kubernetes networking is incredibly powerful but demands strict management. Rely on Ingress Controllers to route public traffic efficiently. Never assume the internal network is secure; deploy strict "Default Deny" Network Policies to isolate workloads. Finally, as microservice complexity scales, transition to a Service Mesh like Istio or Linkerd to abstract the complexities of mTLS, advanced traffic routing, and deep observability away from the application developers.
All in One Place
Atler Pilot decodes your cloud spend story by bringing monitoring, automation, and intelligent insights together for faster and better cloud operations.