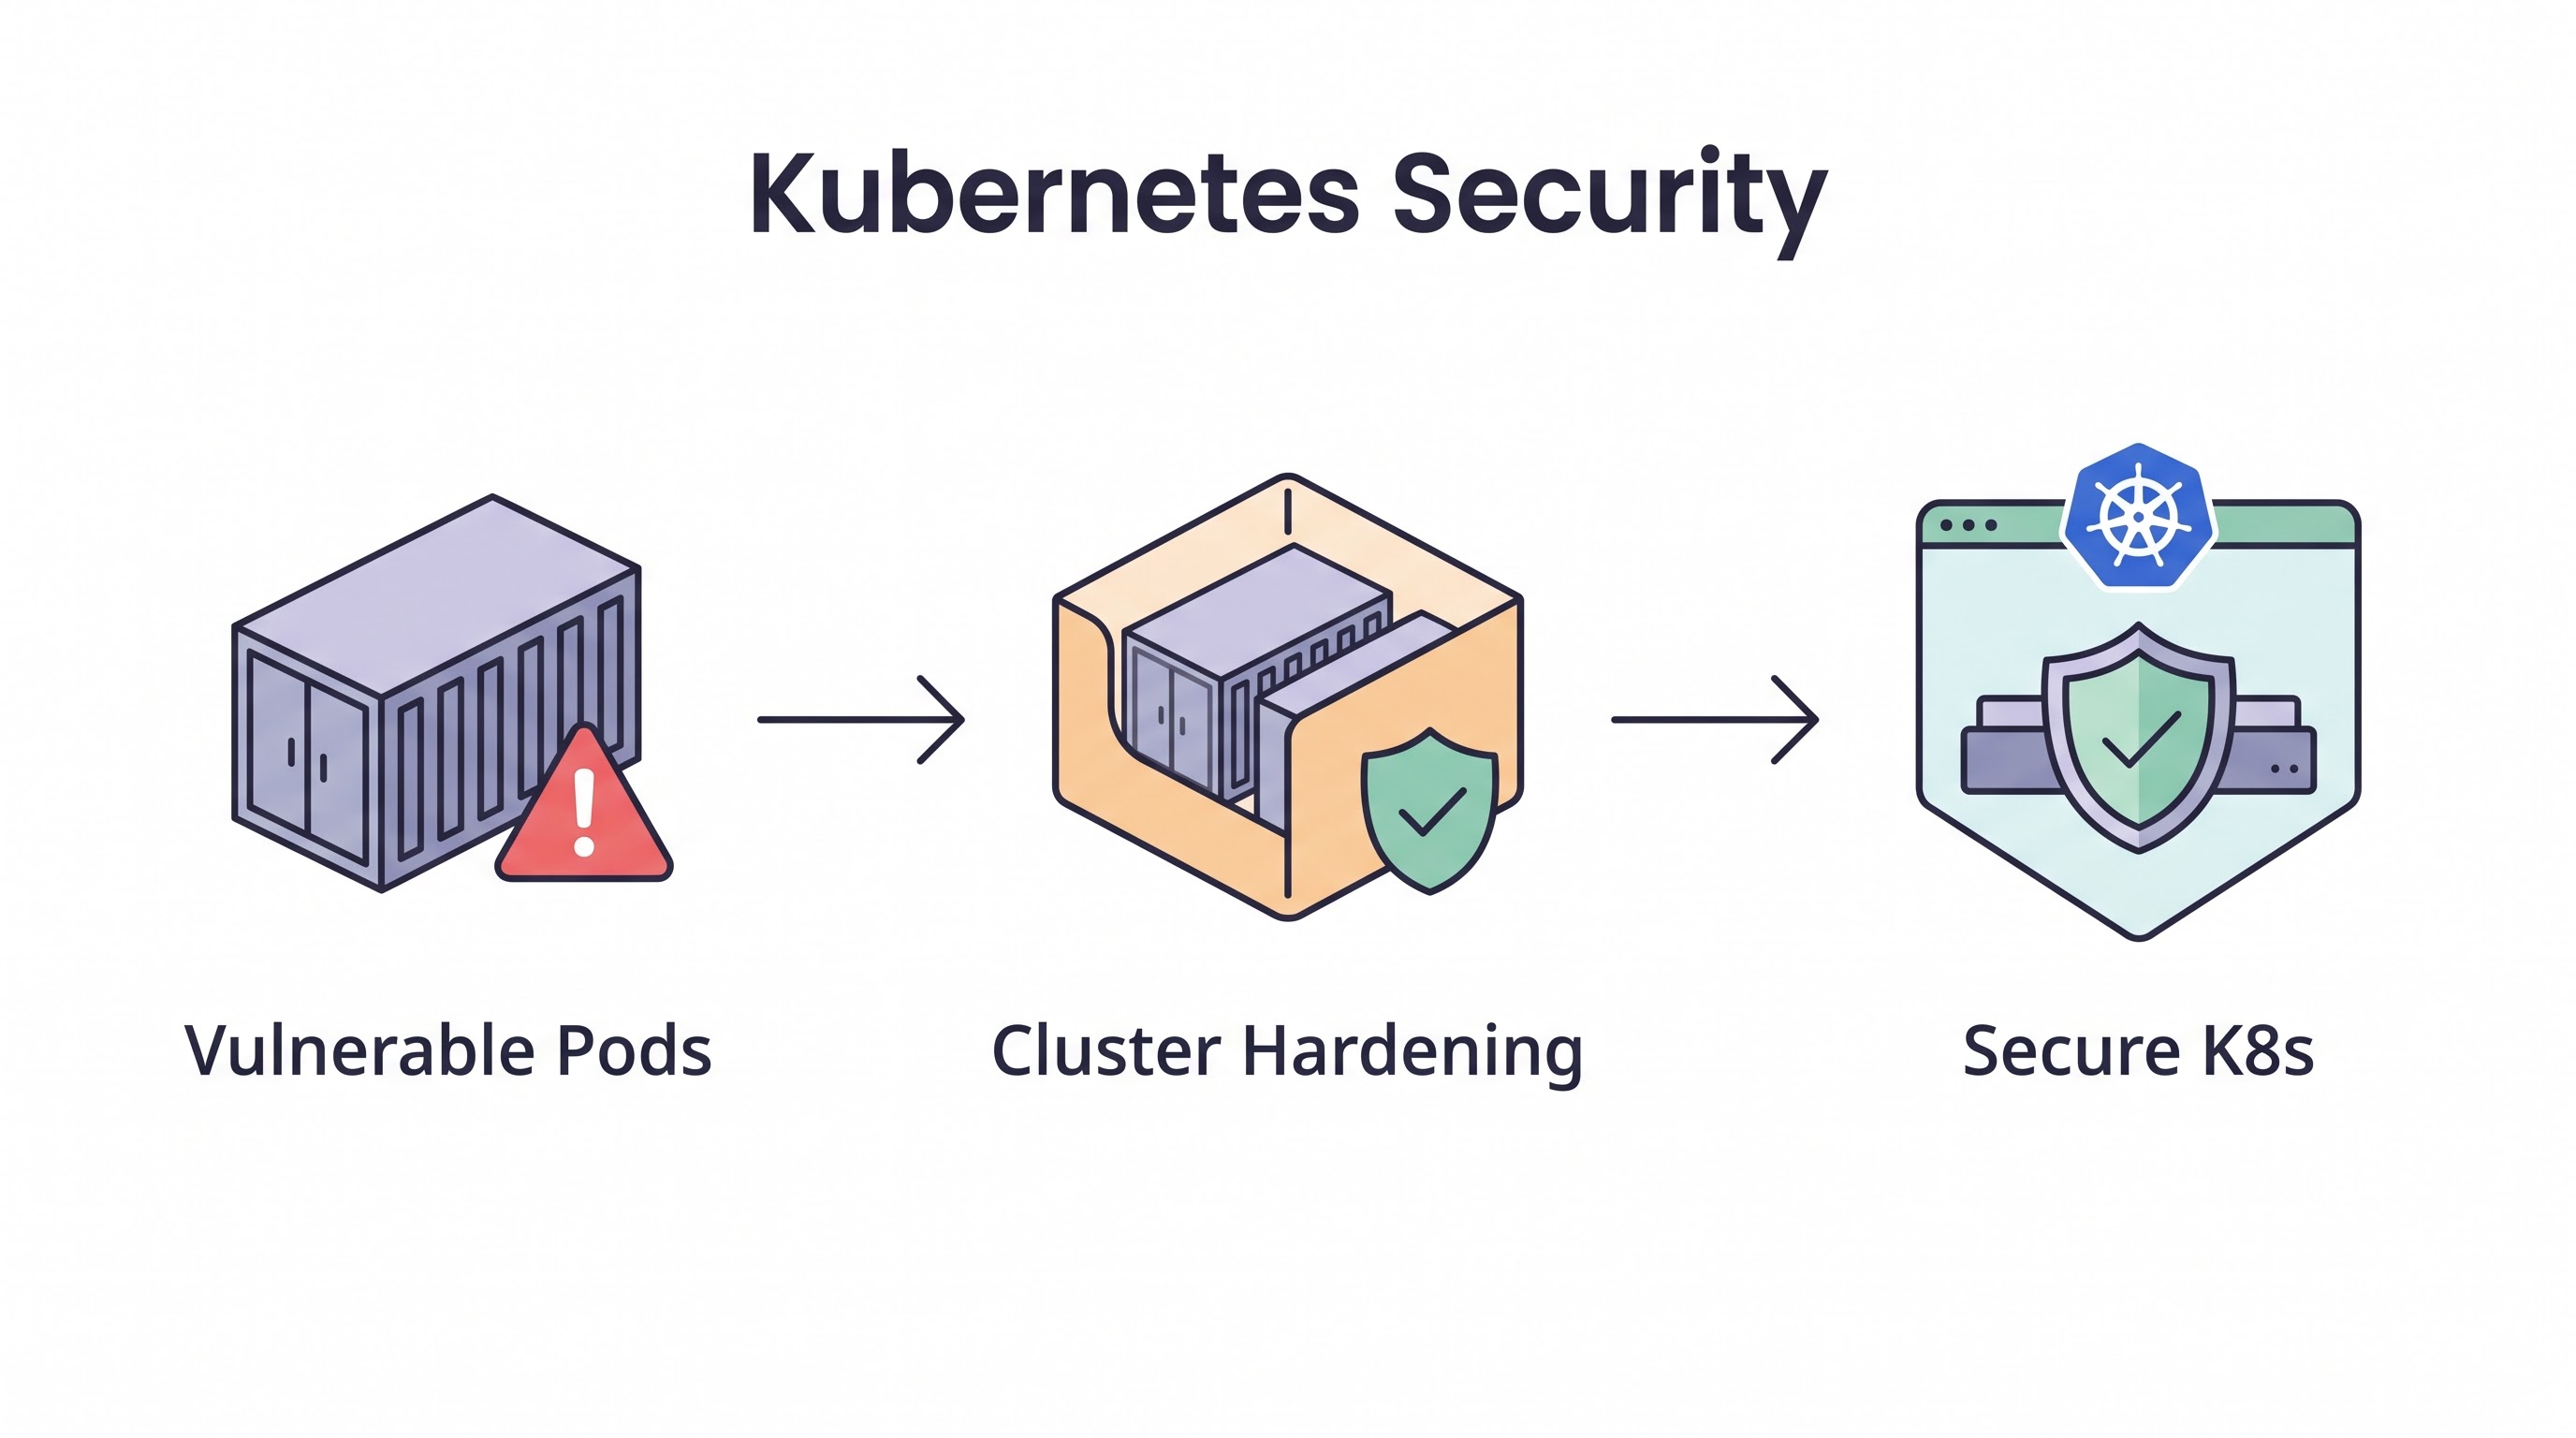
The Complexity of Kubernetes Security
Kubernetes is not just a container orchestrator; it is a distributed, API-driven cloud operating system. Its power lies in its extreme flexibility, but that flexibility requires a massive surface area of configuration. In its default state, Kubernetes is designed for developer velocity, not security. Pods can run as root, every pod can talk to every other pod, and the API server is often dangerously exposed.
Securing Kubernetes requires a defense-in-depth approach. You must secure the cloud infrastructure hosting the cluster (the VMs and network), the Kubernetes control plane, the network traffic between the pods, the configuration of the pods themselves, and finally, the code running inside the containers.
This guide details the architectural necessities for securing modern managed Kubernetes environments (Amazon EKS, Google GKE, and Azure AKS).
Securing the Control Plane
The Kubernetes API server is the brain of the cluster. If an attacker compromises the API server, they own the entire cluster and all its workloads.
Private API Endpoints: Never expose the Kubernetes API server directly to the public internet. Configure your managed cluster (EKS/GKE/AKS) to use a private endpoint. Administrators and CI/CD pipelines must access the API via a VPN, Bastion host, or an Identity-Aware Proxy.
Node Security: The underlying worker nodes (EC2, Compute Engine) must be hardened. Use specialized, minimal container operating systems (like Bottlerocket or COS) rather than full Linux distributions. Ensure nodes are situated in private subnets with strictly scoped Security Groups.
API Auditing: Enable Kubernetes audit logging and forward the logs to a centralized SIEM (like Splunk or AWS CloudWatch). This is your only record of who requested what from the API server.
Mastering Kubernetes RBAC
Role-Based Access Control (RBAC) regulates who can access the Kubernetes API and what actions they can perform. Misconfigured RBAC is a primary vector for cluster compromise.
No Cluster-Admin for Humans: The
cluster-adminrole grants god-mode over the entire cluster. It should only be used by automated CI/CD deployment pipelines, never for daily human operations.Namespace Isolation: Grant developers access only to the specific Namespaces where their applications reside, using
RoleBindingsrather thanClusterRoleBindings.Service Account Least Privilege: Every pod uses a ServiceAccount to talk to the API server. Do not use the
defaultServiceAccount. Create specific ServiceAccounts for specific deployments and grant them only the API permissions they absolutely need (e.g., a monitoring pod needs to "get pods", but a web application pod needs zero API access).
Pod Security and Admission Controllers
You cannot trust developers to write secure pod manifests (YAML). You must enforce security mathematically before the pod is allowed to run.
Pod Security Admission (PSA): Kubernetes natively provides PSA (replacing the deprecated PodSecurityPolicies). Enforce the "Restricted" profile at the namespace level to mandate secure defaults.
Preventing Privilege Escalation: Containers must never run as the root user. Set
runAsNonRoot: truein the SecurityContext. Prevent containers from mounting the underlying host's filesystem, and drop all unnecessary Linux capabilities.OPA Gatekeeper: For advanced policy enforcement, deploy Open Policy Agent (OPA) Gatekeeper. This Admission Controller allows you to write custom rules (e.g., "Deny any pod that pulls an image from Docker Hub instead of our internal private registry").
Network Policies: Micro-segmentation in K8s
By default, the Kubernetes network is flat. If Pod A is compromised, it can ping, scan, and attack Pod B, even if they are in different namespaces.
Network Policies are the firewall rules of Kubernetes. You must implement a "Default Deny" network policy in every namespace, isolating all pods. You then explicitly write policies to allow necessary traffic (e.g., allow the "Frontend" pods to communicate with the "Backend" pods on port 8080, but deny all other connections). This is the foundation of Zero Trust within the cluster.
Handling Secrets in Kubernetes
Kubernetes native Secrets are fundamentally insecure by default; they are merely base64 encoded, not encrypted.
Enable KMS Encryption: You must configure the cluster to encrypt the
etcddatabase (where secrets are stored) using a cloud provider KMS key (e.g., AWS KMS or Azure Key Vault).External Secrets Operators: Best practice dictates not using Kubernetes Secrets at all. Use tools like the External Secrets Operator or HashiCorp Vault to inject secrets dynamically from an external, highly secure vault directly into the pod at runtime, keeping them completely out of the Kubernetes manifest files.
Runtime Security and Threat Detection
Despite perfect configuration, zero-day vulnerabilities in application code will still exist. Runtime security detects malicious behavior while the container is executing.
Deploy tools like Falco (a CNCF project). Falco monitors system calls at the Linux kernel level. If a containerized web application suddenly attempts to spawn a bash shell, modify an executable binary, or open a network connection to an unknown IP address, Falco detects the anomalous system call and triggers an immediate incident response alert, allowing you to kill the compromised pod.
Securing the Container Supply Chain
Cluster security is irrelevant if you deploy malware. As detailed in the DevSecOps Guide, container images must be aggressively scanned for vulnerabilities in the CI/CD pipeline and the container registry. Use Admission Controllers to cryptographically verify image signatures, ensuring that only images built and scanned by your secure pipeline are allowed to execute in the cluster.
Key Takeaway
Kubernetes security demands aggressive restriction. Secure the control plane by isolating the API server. Restrict human and machine access using strict RBAC. Use Admission Controllers like OPA Gatekeeper to mathematically prevent insecure pods (running as root) from executing. Flatten the internal attack surface with "default deny" Network Policies, and deploy runtime monitoring like Falco to detect anomalous behavior inside the containers.
All in One Place
Atler Pilot decodes your cloud spend story by bringing monitoring, automation, and intelligent insights together for faster and better cloud operations.