The Multi-Cloud Delusion
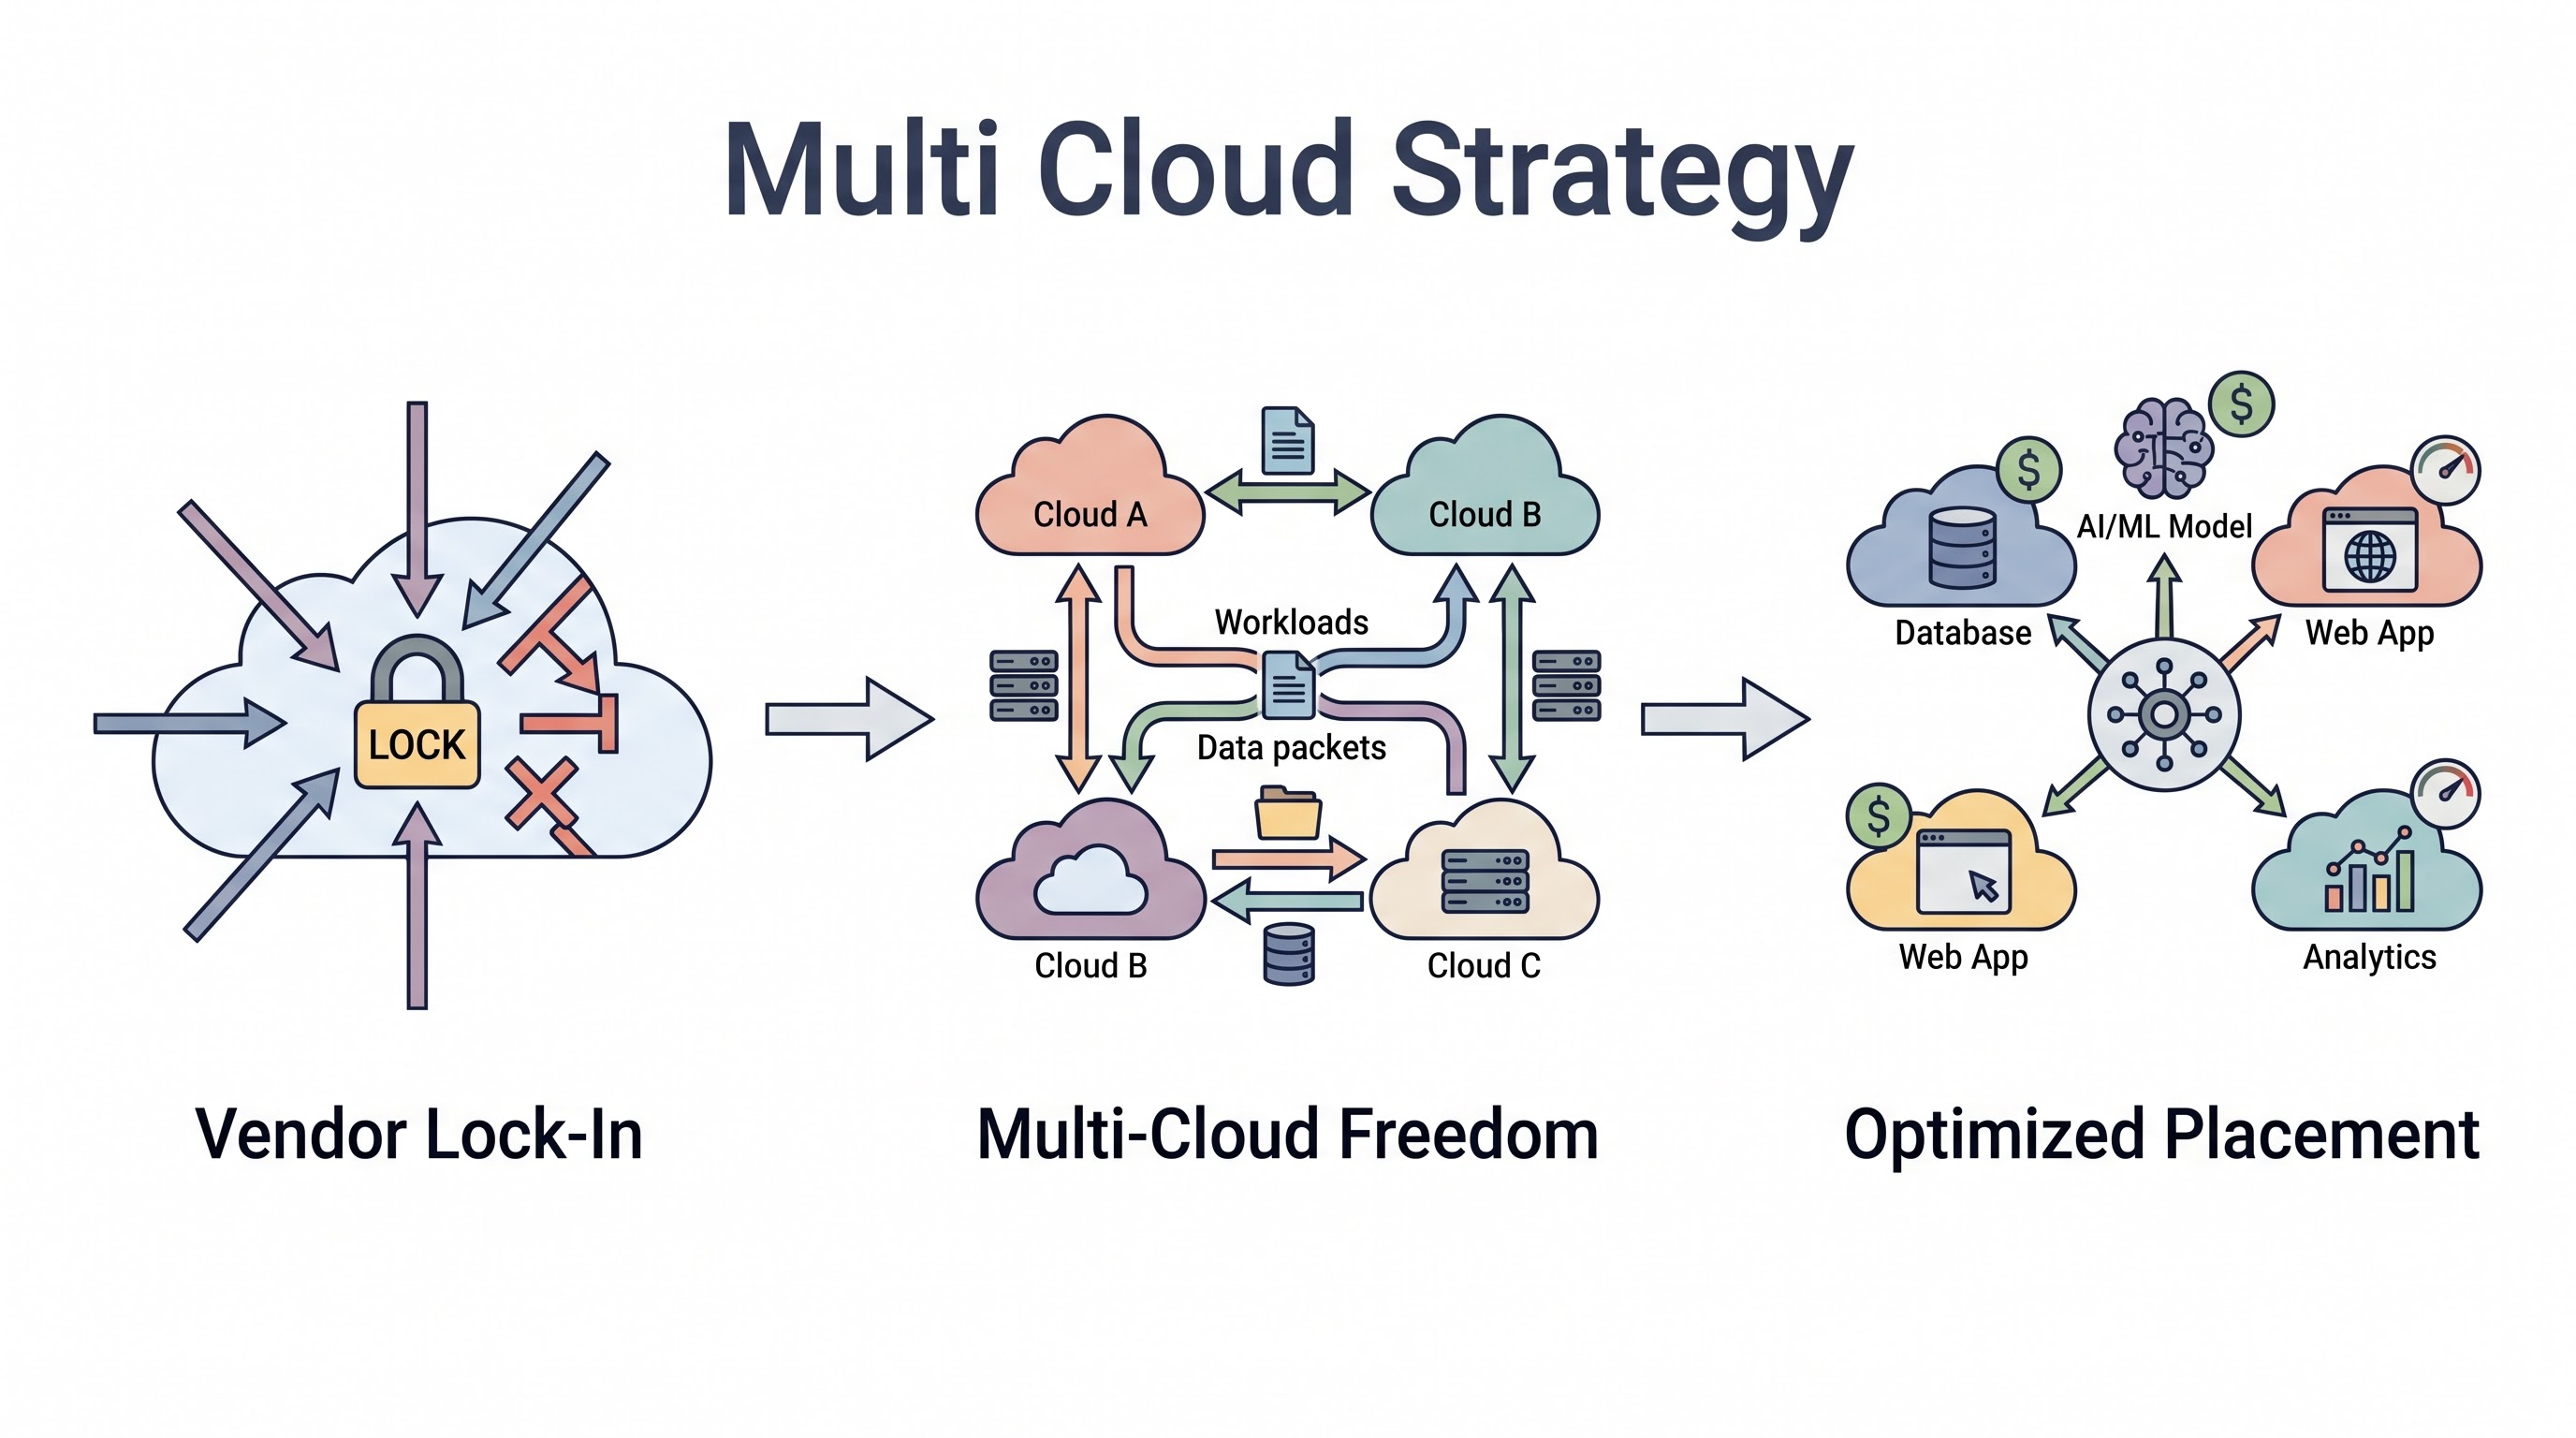
A frequent directive from enterprise boardrooms is the mandate to adopt a "Multi-Cloud Strategy." The logic usually stems from a fear of vendor lock-in or a desire for leverage during contract negotiations with AWS, Azure, or GCP. The theoretical goal is to build an application so portable that it can be seamlessly shifted from AWS to Azure over a weekend to chase cheaper compute prices.
In practice, for 95% of organizations, pursuing an active-active multi-cloud architecture is a catastrophic mistake. It introduces crippling operational complexity, drastically increases security risks, dilutes engineering expertise, and ironically, often results in significantly higher costs.
This guide deconstructs the multi-cloud marketing hype, examining the severe technical and financial realities of spanning cloud providers, while outlining the few narrow scenarios where a multi-cloud strategy is legitimately required.
The Myth of Vendor Lock-in Avoidance
The primary driver for multi-cloud is avoiding vendor lock-in. The assumption is that if you use AWS Lambda or DynamoDB, you are trapped in AWS forever, but if you use generic Kubernetes and PostgreSQL on EC2, you can easily move to GCP.
This ignores the reality of data gravity and cloud integration. Lock-in is not primarily about compute; it is about data, IAM, and networking. Even if your application code is perfectly containerized, moving a 50-terabyte database from AWS to Azure is an expensive, high-risk endeavor that requires significant downtime. Moving IAM policies, rewriting Terraform modules, and re-architecting security groups take months.
More importantly, avoiding vendor lock-in means you cannot use the vendor's best features. You are deliberately refusing to use the highly optimized, managed services (like Spanner, Aurora, or BigQuery) that make the cloud valuable in the first place.
The Hidden Costs of Multi-Cloud
Multi-cloud architectures destroy the core tenets of FinOps.
Loss of Volume Discounts: Cloud providers offer massive discounts (Enterprise Discount Programs) based on total spend. Splitting a $10M budget across AWS and Azure means you get a lower tier of discount from both, raising your baseline costs.
Data Egress Fees: Cloud providers charge nothing to bring data in, but charge heavily to move it out. If your web frontend is on AWS, but it queries a data warehouse on GCP, you are paying massive egress penalties for every megabyte of data traveling across the internet between the two clouds.
Redundant Tooling: You now need to pay for security and monitoring platforms that support multi-cloud, which are inherently more expensive, or you end up running two separate sets of native tools (GuardDuty + Azure Defender), doubling your licensing costs.
The "Lowest Common Denominator" Architecture
To make an application truly portable across clouds, it must be completely infrastructure-agnostic. This forces architects into the "lowest common denominator" approach.
You cannot use AWS SQS, because Azure doesn't have it. You cannot use GCP Pub/Sub, because AWS doesn't have it. Instead, you must deploy, manage, patch, and secure your own Kafka cluster on raw VMs in both clouds. The engineering team spends its time building and maintaining commodity infrastructure instead of building business features. The pursuit of portability destroys developer velocity.
When Multi-Cloud Actually Makes Sense
Multi-cloud is not inherently evil; it is just usually misapplied. There are specific, valid use cases:
Best-of-Breed Analytics/AI: An organization runs its core application infrastructure on AWS, but replicates data nightly to GCP to utilize BigQuery or Google's Vertex AI for specific machine learning workloads because GCP's tooling is deemed superior. This is "multi-cloud by workload," not active-active multi-cloud.
Mergers and Acquisitions: Company A (AWS) buys Company B (Azure). The combined entity is now multi-cloud by default. The strategy should be to secure and manage both, not to forcibly migrate Company B immediately if the Azure environment is stable.
Extreme Regulatory Mandates: Specific government or financial regulations may legally mandate that an organization must be able to survive the complete, total failure of a single cloud provider. (These organizations possess the massive budgets required to engineer this).
The Multi-Cloud DR Fallacy
A common argument is using multi-cloud for Disaster Recovery (e.g., Primary in AWS, DR in Azure). As detailed in the Cloud DR Guide, this is almost always a mistake.
Surviving a regional AWS outage (e.g., us-east-1 going down) is easily solved by failing over to AWS us-west-2. Engineering a failover to a completely different cloud provider requires maintaining two entirely different IaC codebases, two different security postures, and complex cross-cloud data replication. The complexity of the failover process itself is more likely to cause an outage than a global AWS failure.
The Operational Burden
The heaviest tax of multi-cloud is cognitive load. A Cloud Operations engineer must understand AWS IAM, Azure Active Directory, AWS VPCs, and Azure VNets. The security team must write policies for AWS Config and Azure Policy. Finding engineers deeply expert in one cloud is hard; finding engineers expert in two is nearly impossible.
Master One Cloud First
For the vast majority of organizations, the optimal strategy is "Single Cloud Native." Choose one provider (AWS, Azure, or GCP). Go deep. Embrace their proprietary, managed services to maximize velocity and minimize operational overhead. Consolidate your spend to maximize discounts. Do not dilute your engineering talent and security posture attempting to chase the myth of cloud portability unless a specific, best-of-breed workload strictly demands it.
Key Takeaway
Active-active multi-cloud architecture is an anti-pattern that drastically increases cost, operational complexity, and security risk, often resulting in "lowest common denominator" engineering. Organizations should prioritize deeply integrating into a single primary cloud provider to maximize agility and financial discounts. Multi-cloud should only be adopted for specific, isolated, best-of-breed workloads (like AI/ML) where the benefit outweighs the massive integration friction.
All in One Place
Atler Pilot decodes your cloud spend story by bringing monitoring, automation, and intelligent insights together for faster and better cloud operations.