The Shift in the Attack Surface
Serverless architecture (AWS Lambda, Azure Functions) delegates the security of the underlying infrastructure—the physical servers, the hypervisor, the operating system, and the runtime environment—entirely to the cloud provider. From a security perspective, this is a massive advantage. You no longer need to worry about patching Linux kernel vulnerabilities.
However, serverless does not mean "security-less." The attack surface merely shifts. Instead of exploiting the operating system, attackers exploit the application logic, the event triggers, and the highly permissive IAM roles frequently attached to serverless functions.
Because serverless environments consist of hundreds of tiny, interconnected functions communicating via events, traditional network firewalls and endpoint security agents are useless. Security must be embedded directly into the code and the cloud configuration. This guide outlines how to secure modern serverless architectures.
The Primary Threat: Event Data Injection
In traditional web applications, SQL injection or Cross-Site Scripting (XSS) occurs via HTTP requests. In serverless, functions are triggered by a massive variety of events: HTTP requests (via API Gateway), S3 bucket uploads, DynamoDB streams, or SQS messages.
Attackers can inject malicious payloads into any of these event sources. If a Lambda function processes an uploaded image filename from S3 without sanitizing the input, an attacker could upload a file named image.jpg; rm -rf /. If the function executes a system command using that filename, it suffers a Command Injection attack.
The Mitigation: Developers must treat all event data as untrusted, regardless of the source. Rigorous input validation and sanitization libraries must be applied to the event payload before any processing occurs.
Execution Roles: The Principle of Least Privilege
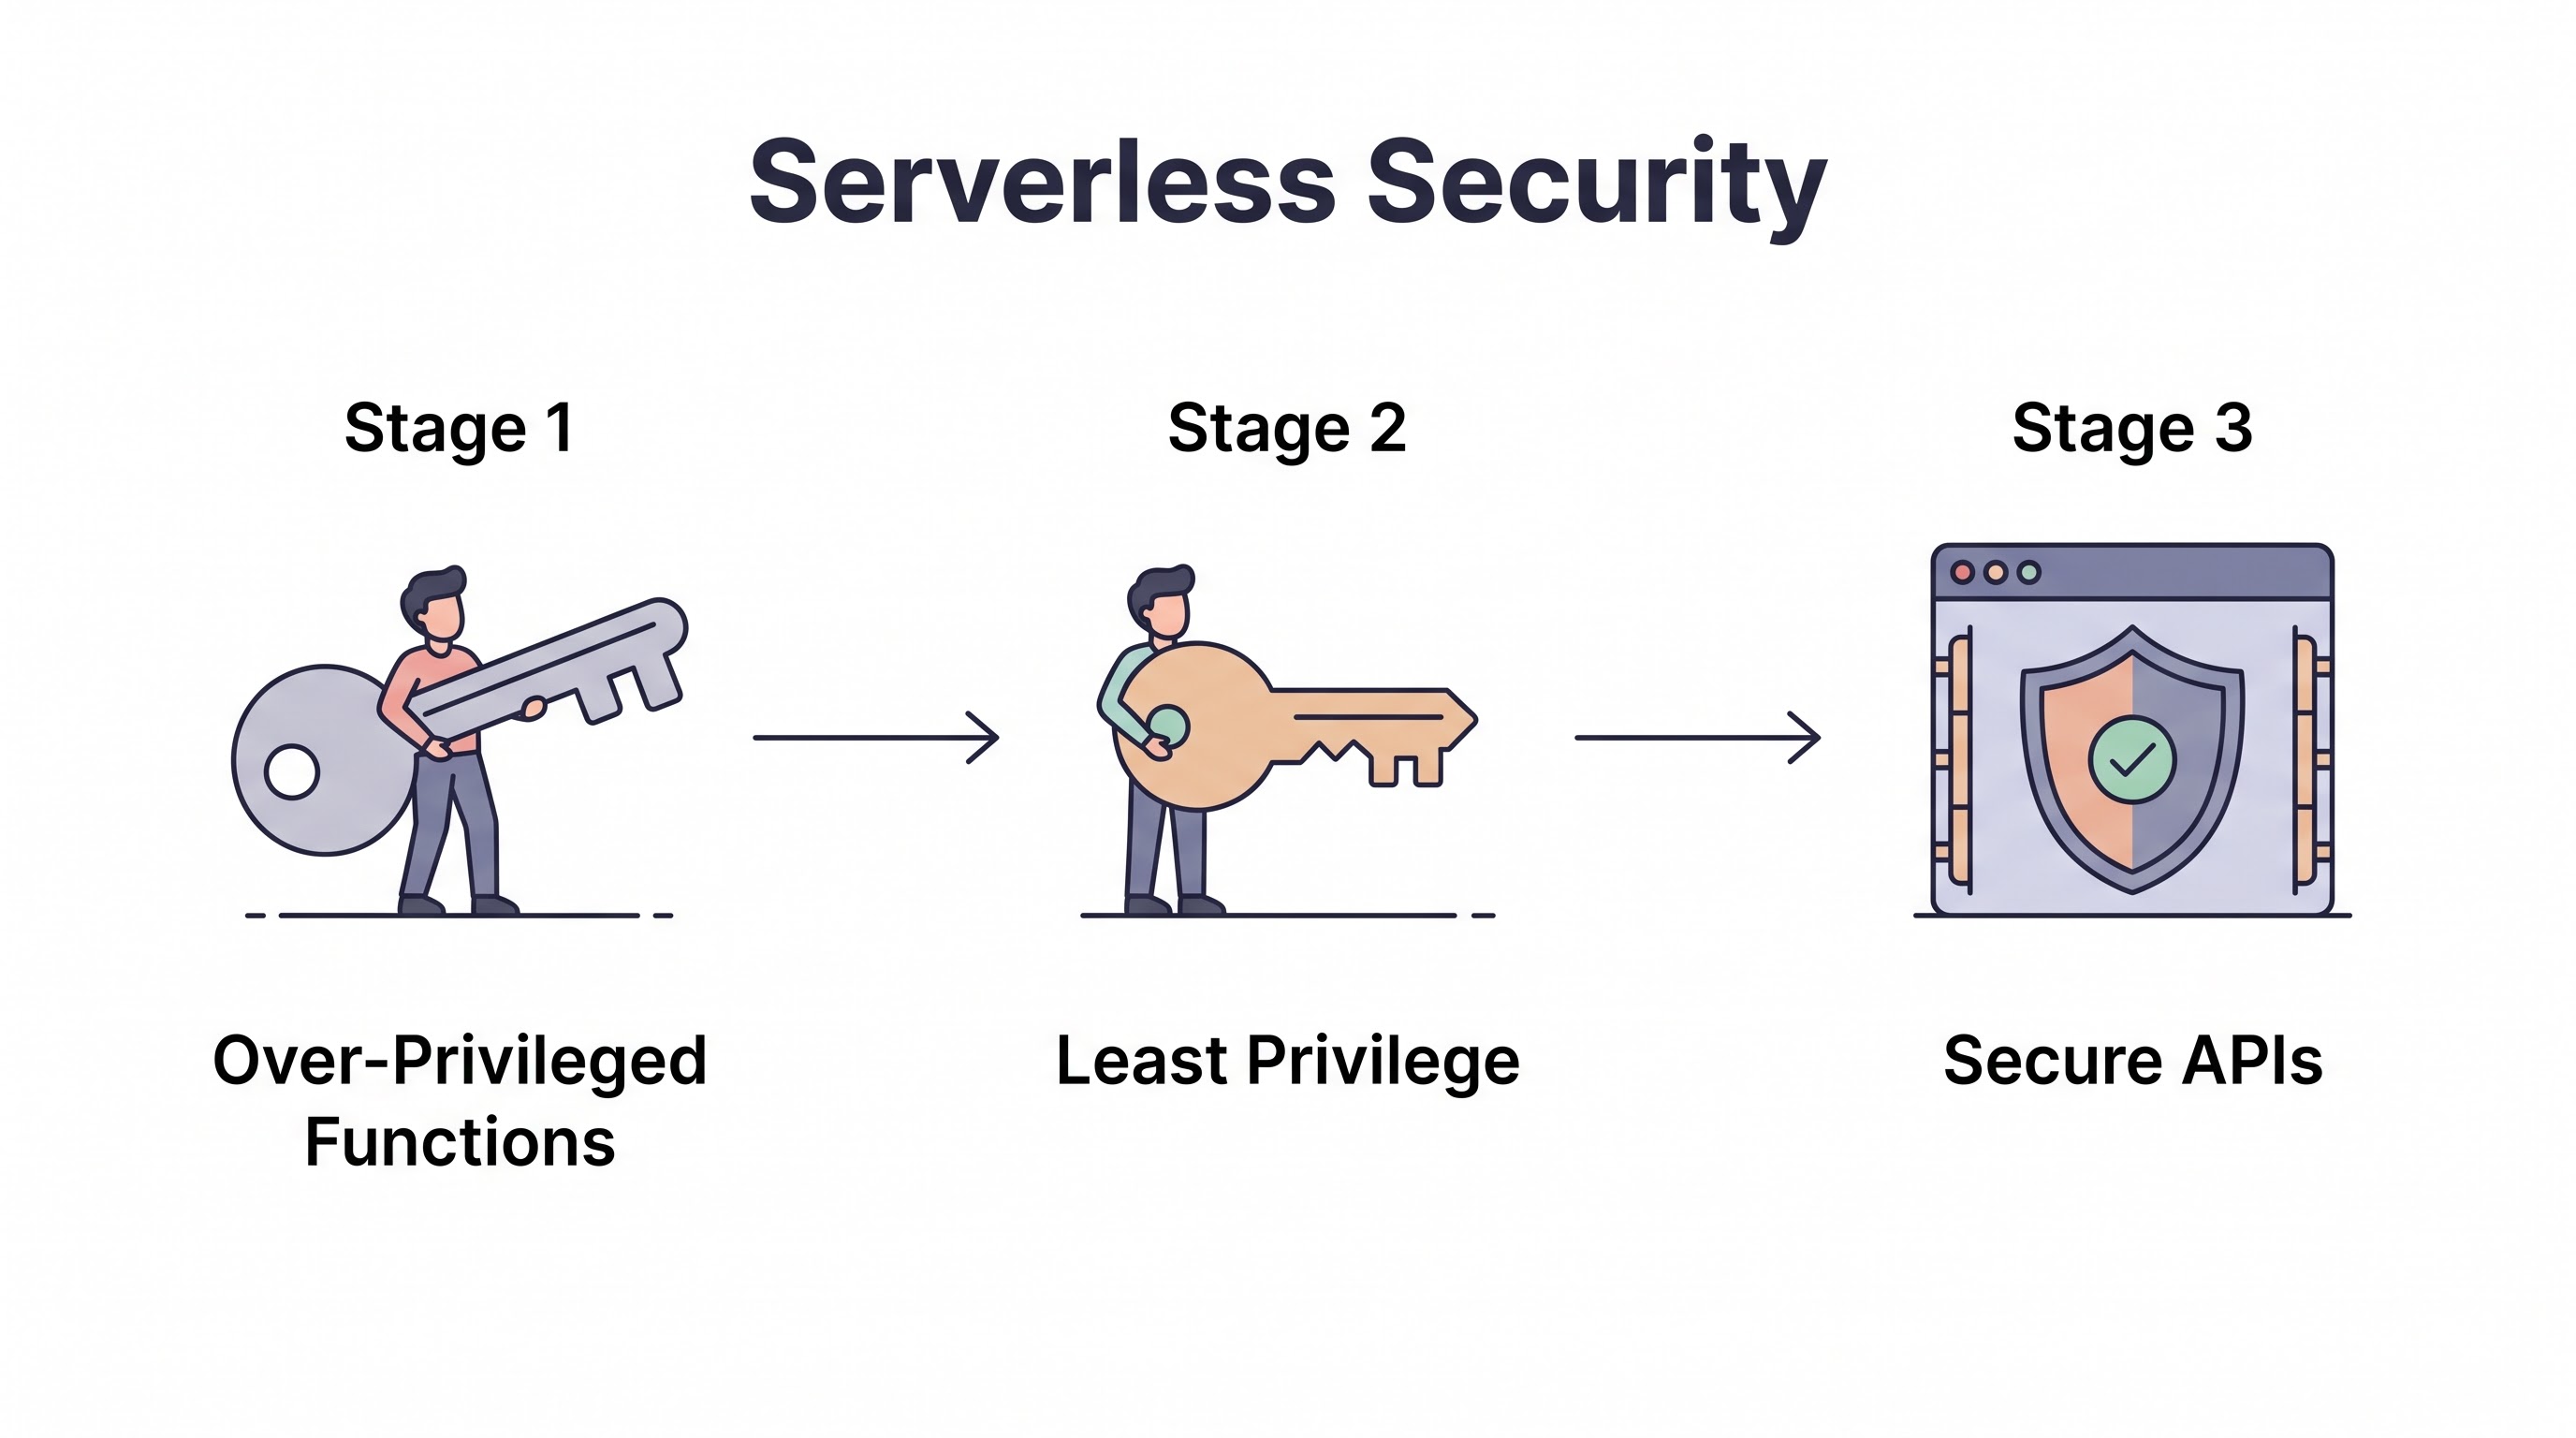
The most devastating serverless breaches are caused by over-privileged Execution Roles.
When creating a Lambda function, it is tempting to attach an IAM role with AmazonS3FullAccess and AmazonDynamoDBFullAccess to avoid permission errors during development. If an attacker discovers a code injection vulnerability in that function, they instantly inherit those full access permissions, allowing them to delete every S3 bucket in the account.
The Mitigation: Implement radical least privilege. A Lambda function's Execution Role should be mathematically precise. It should only be allowed to perform specific actions (e.g., s3:PutObject) on a specific resource (e.g., arn:aws:s3:::specific-bucket-name/*). Each of your 100 Lambda functions must have its own unique, custom-tailored IAM role.
Securing the API Gateway Front Door
For synchronous serverless applications, the API Gateway is the front door. It must be heavily fortified.
Web Application Firewall (WAF): Always deploy AWS WAF (or Azure Front Door) in front of your API Gateway to block common OWASP Top 10 attacks and rate-limit aggressive bots.
Authentication: Never leave an API endpoint open to the internet unless strictly necessary. Utilize Amazon Cognito, Auth0, or custom Lambda Authorizers to validate JWT tokens before the request is allowed to reach the backend Lambda function.
Request Validation: Configure API Gateway to perform schema validation. If the API expects an integer for an ID, and the client sends a SQL injection string, the API Gateway should reject the request before the Lambda function is ever invoked, saving both compute resources and security risk.
The Vulnerability of Dependencies
A typical Node.js Lambda function contains a few hundred lines of custom code and hundreds of thousands of lines of code imported via npm packages. Attackers frequently target the software supply chain, hiding malicious code within popular open-source libraries.
The Mitigation: Integrate Software Composition Analysis (SCA) into your DevSecOps pipeline. Tools must scan the deployment package (the zip file or container image) for known CVEs in third-party libraries and block the deployment if vulnerabilities are found. Furthermore, keep your function runtimes updated (e.g., migrating from Node 16 to Node 20) to ensure you are utilizing patched environments.
Denial of Service and Denial of Wallet
Serverless elasticity is a double-edged sword. If an attacker launches an HTTP flood against your API Gateway, AWS will cheerfully spin up 10,000 concurrent Lambda functions to handle the traffic. The service won't go down (Denial of Service), but your monthly bill will explode (Denial of Wallet).
The Mitigation:
Set strict Rate Limiting and Throttling rules on the API Gateway.
Configure Reserved Concurrency on your Lambda functions. This sets a hard limit on the maximum number of concurrent executions for a specific function, acting as a financial circuit breaker against runaway scaling.
Utilize Cloud Cost Anomaly Detection to alert the team immediately if serverless spend spikes unexpectedly.
Secrets Management in Ephemeral Compute
Never hardcode API keys or database passwords in Lambda environment variables. Environment variables are often visible in plaintext within the AWS console and can be logged accidentally.
Store all sensitive credentials in AWS Secrets Manager or AWS Systems Manager Parameter Store. The Lambda function should use its Execution Role to retrieve the secret dynamically via an API call during its initialization phase. To prevent high API costs and latency, utilize the AWS Parameters and Secrets Lambda Extension, which automatically caches the secrets locally within the execution environment.
Logging and Tracing the Invisible
Because you cannot install traditional security agents on Lambda, visibility relies entirely on logging and tracing.
Ensure all functions log output to CloudWatch (or Azure Monitor). More importantly, utilize distributed tracing (AWS X-Ray, Datadog) to visualize the path of an event across multiple services. If a compromised function begins making outbound HTTP calls to a suspicious IP address, or attempts to access a DynamoDB table it shouldn't, tracing and log analytics are your only mechanisms for detecting the anomaly.
Key Takeaway
Serverless security requires shifting focus from infrastructure to application logic and access control. Treat every event trigger as a potential injection vector. Implement radical least privilege by assigning unique, microscopic IAM roles to every function. Protect against "Denial of Wallet" attacks by enforcing API rate limits and Lambda concurrency limits, and aggressively scan all third-party code dependencies before deployment.
All in One Place
Atler Pilot decodes your cloud spend story by bringing monitoring, automation, and intelligent insights together for faster and better cloud operations.