The Dashboard of Despair
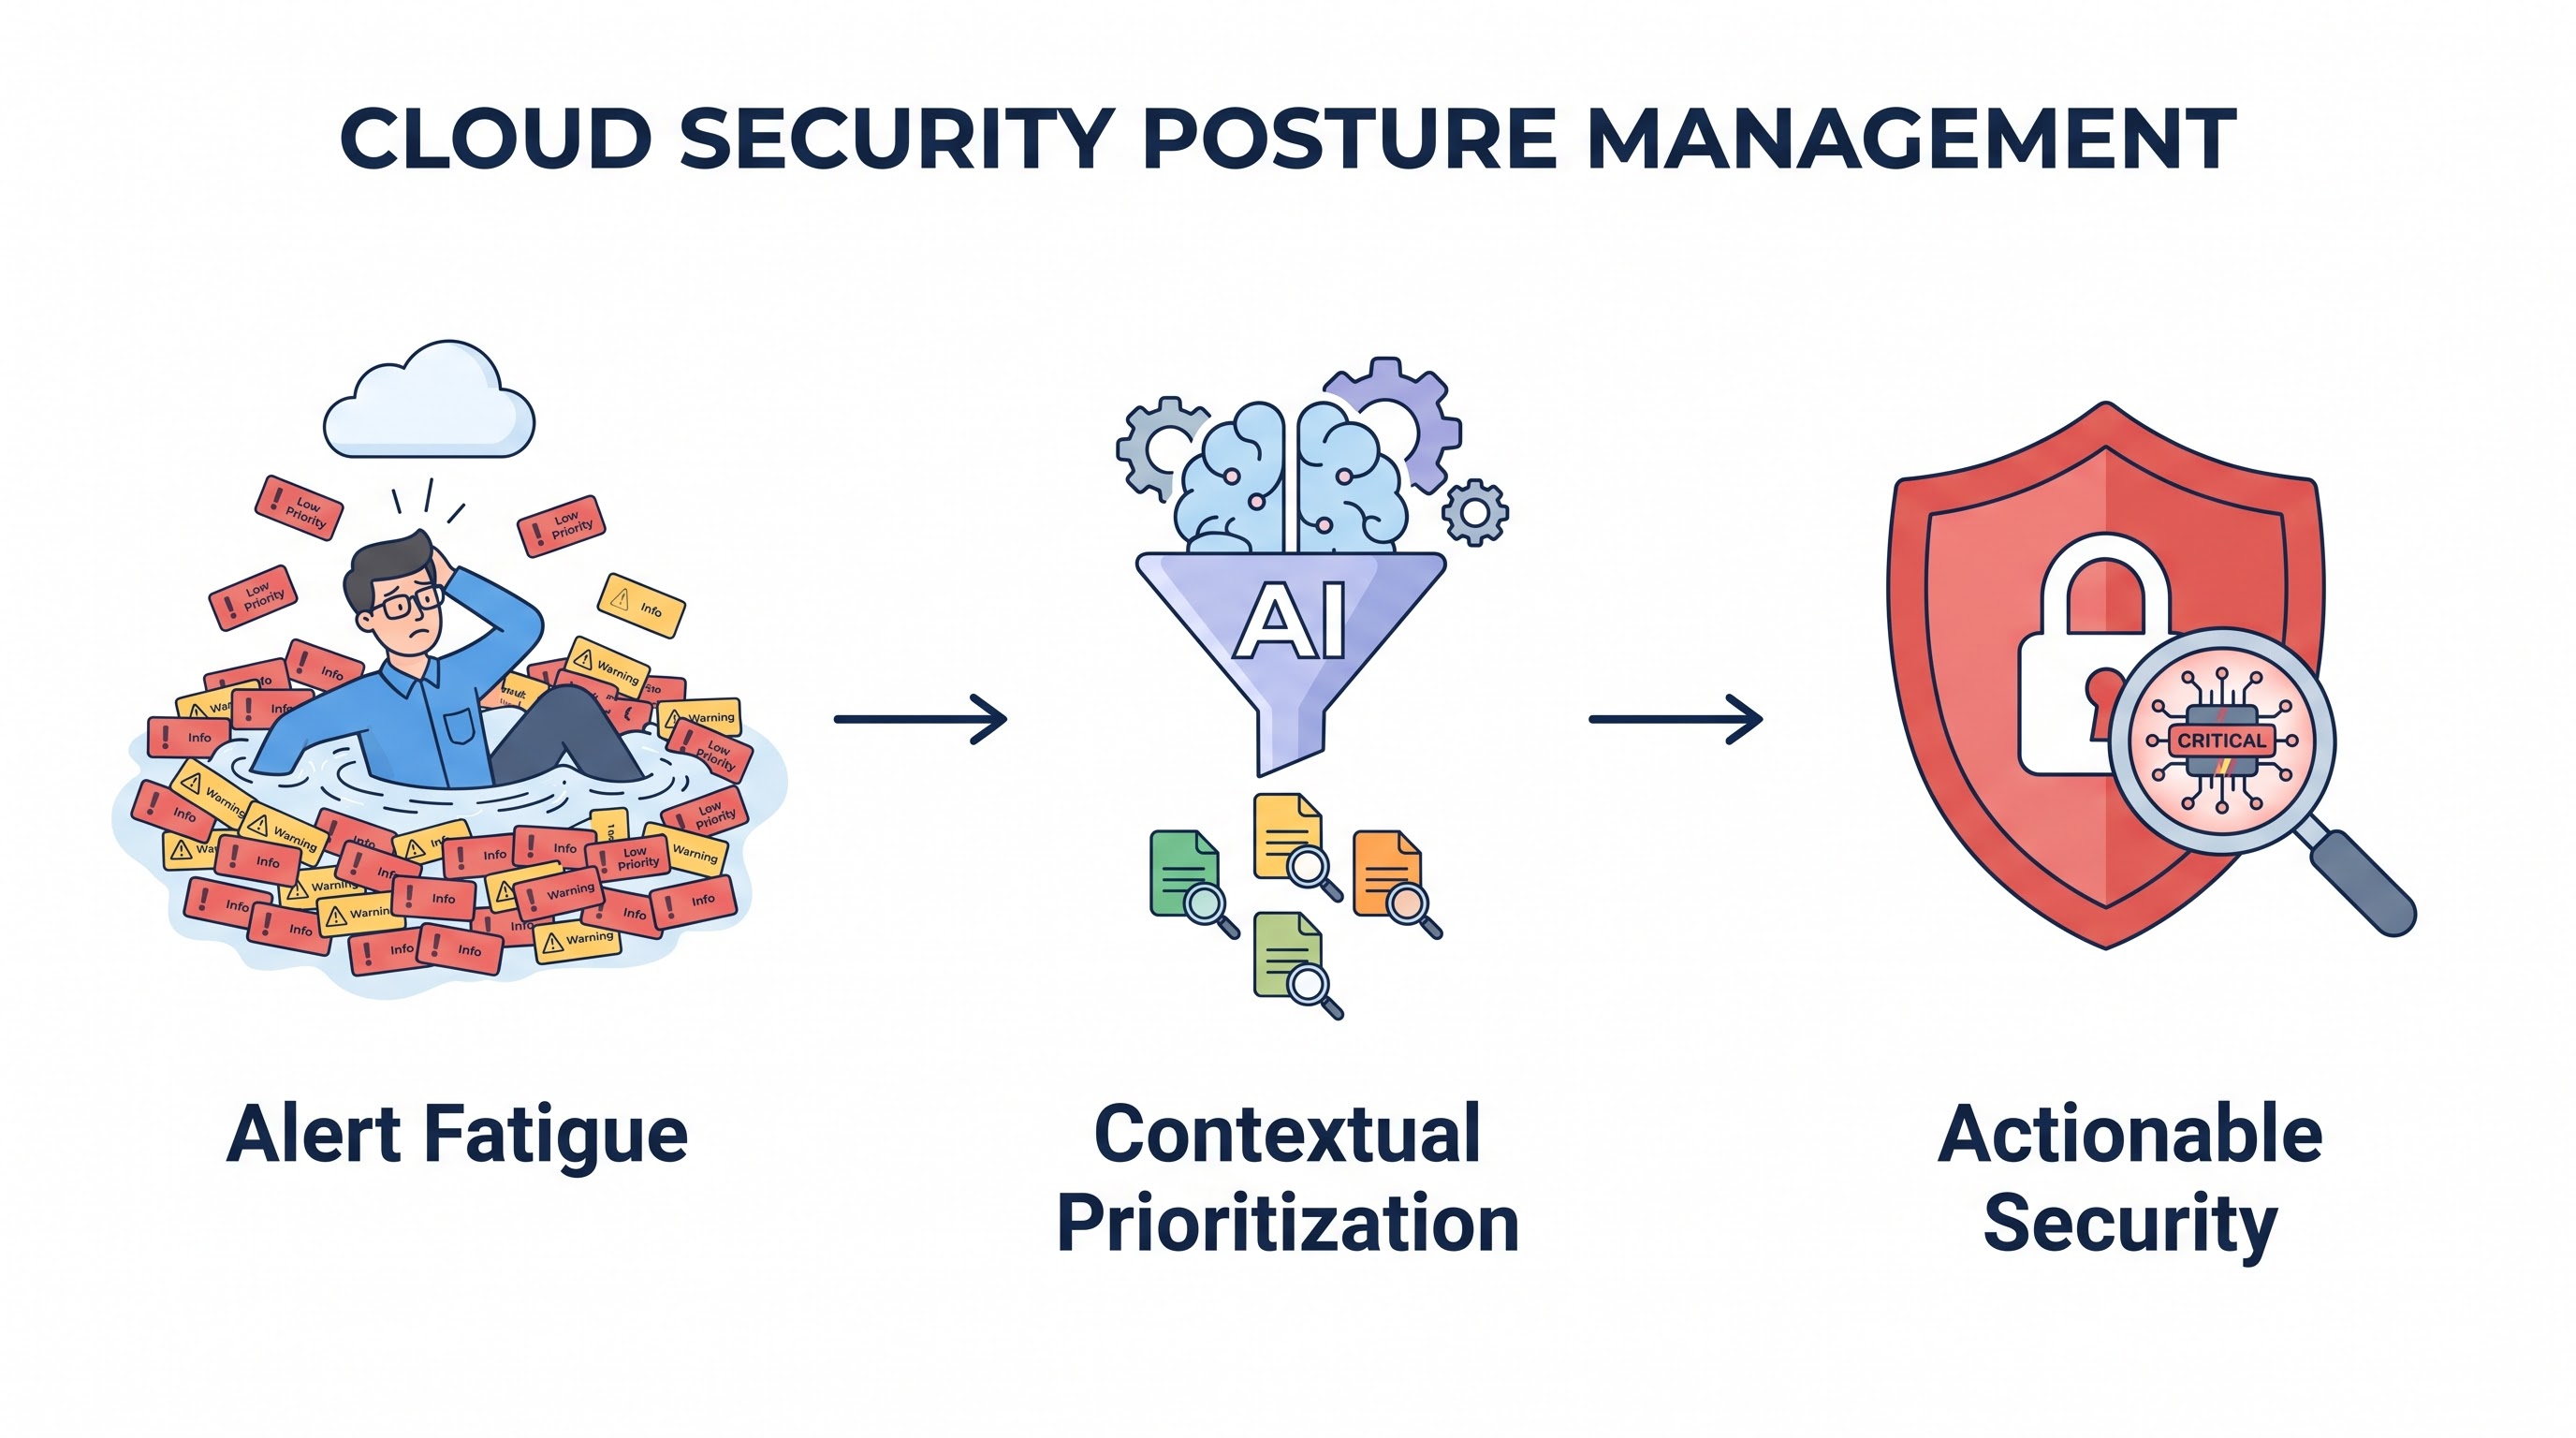
The deployment of a new Cloud Security Posture Management (CSPM) platform usually follows a predictable and depressing arc. Week 1: Excitement over unprecedented visibility into the cloud environment. Week 2: Panic as the initial scan reveals 45,000 "Critical" and "High" severity misconfigurations. Week 4: Exhaustion as the security team desperately tries to create Jira tickets for every alert. Week 8: Apathy. The DevOps team starts routing all security alerts directly to the trash folder. The tool becomes shelfware.
This is the epidemic of alert fatigue. A security tool that alerts on everything effectively alerts on nothing. When engineers are overwhelmed by noise, they invariably miss the single, faint signal indicating a true breach.
The problem is not the concept of CSPM; continuous monitoring is mandatory for cloud security. The problem is implementation. This guide details how to tune your CSPM to transform it from a noise generator into an actionable, high-signal security engine.
Why CSPMs Generate So Much Noise
Out-of-the-box, a CSPM acts like a highly pedantic auditor. It compares every single resource in your AWS, Azure, and GCP accounts against hundreds of rules defined by frameworks like CIS, NIST, or SOC 2. It lacks business context.
To a raw CSPM scan, an unencrypted S3 bucket containing public website images is a "High Severity Violation" because the CIS benchmark mandates encryption at rest. To the business, that bucket is working exactly as intended, and the risk is zero. If you force your engineers to investigate hundreds of these false positives, you destroy their trust in the tool.
Strategy 1: Contextual Prioritization (The Blast Radius)
Modern CSPM platforms (often categorized as CNAPPs) must analyze the relationships between resources, not just the resources in isolation. You must tune your alerts based on the "Blast Radius."
Consider a vulnerable EC2 instance missing a critical OS patch.
Scenario A: The instance sits in a private subnet, has no route to the internet, and has an IAM role that only allows it to write logs to CloudWatch. (Low Priority).
Scenario B: The instance sits in a public subnet, has port 443 open to the internet, and has an IAM role that allows it to read sensitive customer data from an RDS database. (Critical Priority).
If your CSPM treats both scenarios as equal "High" severity alerts based solely on the CVSS score of the unpatched vulnerability, it is configured incorrectly. Alerts must only be routed to engineering if the combination of network exposure, IAM privileges, and vulnerability status creates an exploitable attack path.
Strategy 2: Environment-Based Suppression
The security requirements for a production banking application are different from those of a developer's sandbox account.
You must integrate your cloud tagging strategy deeply into the CSPM. Create suppression rules that aggressively downgrade or ignore specific alerts in non-production environments.
Rule Example: If an EC2 instance lacks a required monitoring agent, AND the account is tagged
Environment: Sandbox, suppress the alert.Rule Example: If an S3 bucket is unencrypted, AND the bucket is tagged
DataClassification: Public, suppress the alert.
By filtering out the noise from development environments, you ensure that when an alert fires for a Production tagged resource, the engineering team knows it is legitimate.
Strategy 3: The "Known Exception" Workflow
In enterprise architecture, there will always be legitimate business reasons for violating a best practice. Perhaps a legacy vendor application strictly requires port 21 (FTP) to remain open, violating a core security rule.
If the CSPM alerts on this open port every single day, it trains the team to ignore the dashboard. You must build a rigorous "Exception Management" workflow.
The DevOps team requests an exception for the specific resource and rule, providing business justification.
The Security/Risk team approves the exception for a defined time period (e.g., 90 days).
The CSPM is configured to suppress that specific alert for that specific resource until the expiration date.
This keeps the active alert queue clean, ensuring it only contains novel, unreviewed risks.
Strategy 4: Shifting Left to Prevent Noise
The most effective way to handle a CSPM alert is to prevent the misconfiguration from ever reaching the cloud.
As outlined in the DevSecOps Guide, integrate the CSPM's policy engine into the CI/CD pipeline (Infrastructure as Code scanning). If a developer writes a Terraform script that creates an S3 bucket without encryption, the pipeline should fail the build and provide the developer with the necessary code to fix it locally.
This prevents the misconfiguration from being deployed, meaning the runtime CSPM never generates an alert, keeping the security dashboard clear for advanced threats.
From Auditor to Enabler
A CSPM should not be a weapon used by the security team to bludgeon the DevOps team with compliance reports. It must be an operational tool. By prioritizing alerts based on contextual attack paths, aggressively suppressing false positives using tags, managing exceptions rigorously, and shifting detection into the CI/CD pipeline, organizations can transform their CSPM into a high-signal early warning system.
Key Takeaway
Alert fatigue is the enemy of security. Stop routing raw, out-of-the-box CSPM alerts directly to engineering. Security teams must invest the time to tune the platform, suppressing low-context warnings and utilizing cloud tags to filter out development noise. Only send alerts that represent actual, exploitable risk paths in production environments.
All in One Place
Atler Pilot decodes your cloud spend story by bringing monitoring, automation, and intelligent insights together for faster and better cloud operations.